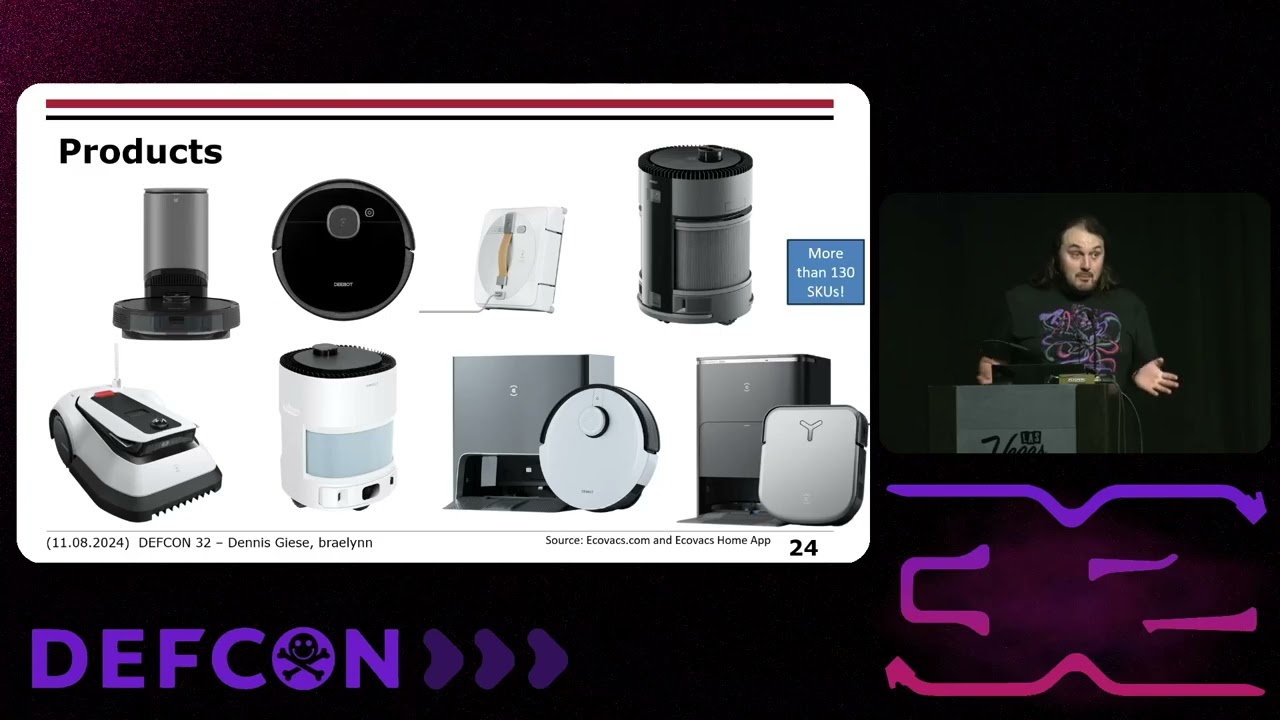
DEF CON 32 - Reverse engineering and hacking Ecovacs robots - Dennis Giese, Braelynn Hacker
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 41:42
The video exposes severe security and privacy flaws in Ecovox IoT devices, enabling remote root access and unauthorized control via unsecured Bluetooth, unencrypted data storage, and misconfigured TLS. 3:45
Key Takeaways:
• Bluetooth LE protocols in Ecovox robots allow remote code execution via command injection, enabling reverse shells up to 100 meters away 35:20
• Devices store unencrypted user data, including Wi-Fi credentials, live video pins, and audio logs, with no access controls on cloud-stored maps or video feeds 22:01
• TLS is misconfigured in both apps and robots, accepting self-signed certificates and allowing man-in-the-middle attacks, exposing authentication tokens for up to seven days 24:11
• PIN verification is client-side and vulnerable to spoofing, allowing bypass of authentication and unsecured video access 32:06
• Root access is achievable on most models via firmware modification, with persistence enabled through auto-start folders on unencrypted data partitions 39:05
Despite certifications, Ecovox devices suffer from fundamental security failures, with data retained indefinitely and no vendor accountability. 41:12
Sources:
- 3:45 Discussion of root access and remote attack vectors
- 35:20 Demonstration of Bluetooth-based command injection and reverse shell
- 22:01 Data storage and cloud access issues, including unencrypted logs
- [24:11](https://www.youtube.com/watch?v=_wUsM0Mlenc&
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
hello everyone uh Welcome to our talk about the reverse engineering of and tacking of echovox robots uh thank you for being here at this time um I know it's kind of loud but uh I hope we figured it out so um before we start um I would like to introduce ourselves uh so first uh I'm Dennis I'm a security researcher or you know also a hardware hacker um and I'm primarily looking into Wireless under bettered security and privacy so I try to look at any device which kind of is interesting for me so I try to reverse engineer everything which kind of basically around us um you might know me as a vacuum and uh iot collector so I have like probably over 600 700 iot devices and 60 or 70 vacuum robots that start counting um and my general goal is to get root access and rout uh vacuum robots um I have…