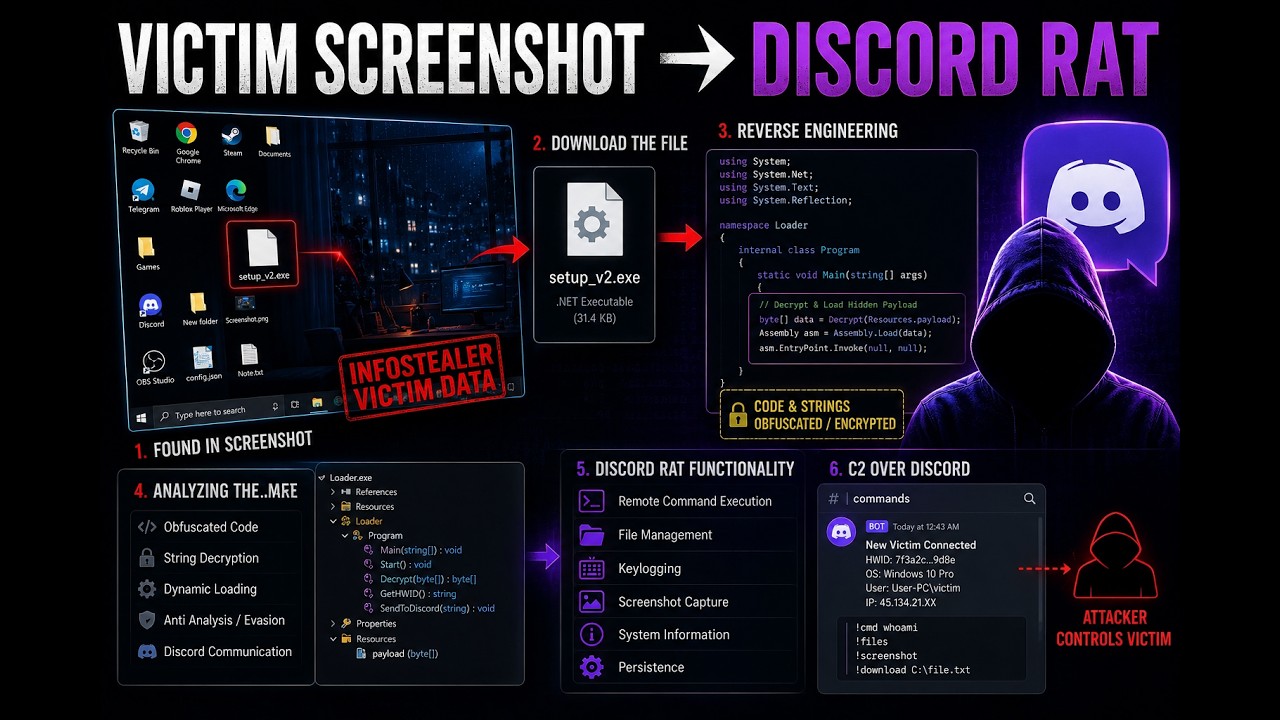
From Victim Screenshot to Discord RAT | Reverse Engineering a Hidden .NET Malware
Source: YouTube · Malware Research Diary · published Jun 8, 2026 · 24:14
BLUF: The video analyzes a malware sample named "Velocity," identified as an infostealer that compromised a user who downloaded it from gofar.io 1:09.
Key Takeaways:
• The investigator obtained a file suspected of being an infostealer after observing an infected user's screenshot 0:14.
• The infected user visited gofar.io and downloaded a file named "Velocity" 0:32.
• Analysis confirms the file is a .NET executable that remains active and downloadable 1:04.
• The infostealer captures screenshots from the victim's computer to exfiltrate data 0:24.
This case highlights the risks of downloading unverified software from obscure sites.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone, welcome back. Today we're just going to do a quick um look up into this files. So, um I obtained this file last week um where it seemed to be an infostealer um being um this this computer been um infected with an infostealer. And this infostealer taking a screenshot and from that screenshot showed that um the infected user went to um gofar.io download a file called Velocity. And from from this is we we can conclude that this is likely is going to be the file that um is a malware that compromised the user. So, let's take a quick look and see what it is. Um just hope it's still up and running. OCP 3, okay. So, the file is still running, I'm still um available to download, so let's take a look. Okay. Velocity is a .NET file. Um fairly small, um about 91 KB. Um so, it's very li…