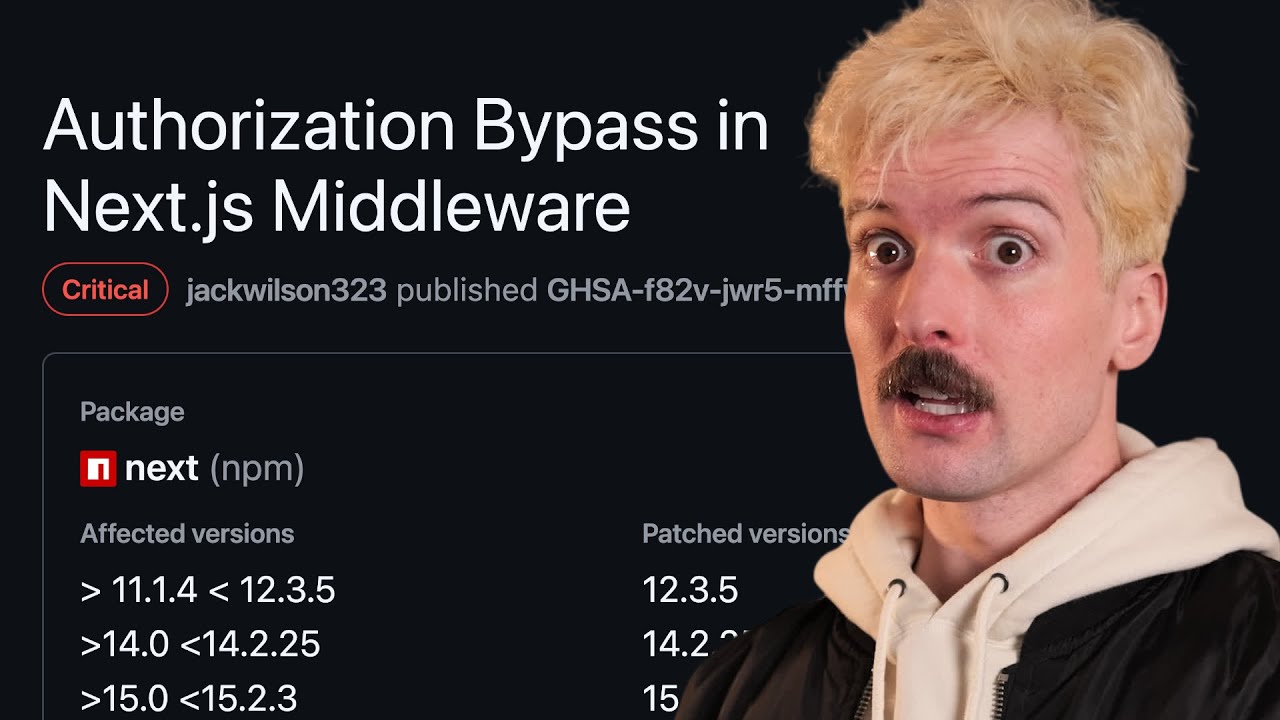
Vercel screwed up (breaking down the Next.js CVE)
Source: YouTube · Theo - t3․gg · published Mar 27, 2025 · 49:07
The Next.js middleware vulnerability allows attackers to bypass authentication checks using a specific header 0:00-0:09, but the impact is limited because middleware shouldn't be used as the primary security layer 8:47-9:00.
Key Takeaways:
• Next.js middleware is poorly named and functions more as a "route interceptor" than traditional middleware 7:27-7:53
• The vulnerability works by adding the "x-middleware-subrequest" header to bypass middleware checks 5:26-6:56
• Proper security should be implemented at the data access layer, not in middleware 13:05-13:25
• Next.js is a primitive framework that requires developers to build their own authentication systems rather than providing a complete solution 37:30-37:52
While the vulnerability caused significant concern, well-architected Next.js applications that implement proper authentication at the data access layer were not actually at risk.
Sources:
- 0:00-0:09 Introduction to the Next.js middleware vulnerability
- 7:27-7:53 Explanation of why middleware is poorly named
- 5:26-6:56 Demonstration of the exploit
- 13:05-13:25 Proper security implementation recommendation
- 21:00-21:36 Why most apps weren't vulnerable
- 37:30-37:52 Description of Next.js as a primitive framework
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
By now, you've probably heard about the Next.js security incident. Middleware can effectively be skipped entirely. This is really, really bad, putting hundreds of thousands of Next apps at risk, right? There is a lot of subtlety here that we have to dig into. There's a lot of things Verscell did absolutely wrong, and I am excited to roast them indefinitely for it. But there are other things here that are just fundamentally being misunderstood. And for what it's worth, I've never seen an app that would have been vulnerable to this, despite the fact that I've audited literally hundreds of Nex.js apps. That doesn't mean this is okay, but it does make the characteristics of the exploit so much more interesting. So, if you want a video that's just going to bash forcell endlessly for bothering t…