Black Hat Asia 2026 | Payload Compromised: Full Key Recovery in Rocket.Chat E2EE
Source: YouTube · Black Hat · published Aug 30, 2026 · 36:33
The research demonstrates that Rocket Chat’s end-to-end encryption (E3EE) is fundamentally broken due to weak password generation and lack of forward secrecy, allowing attackers with server access to decrypt all messages 0:30.
Key Takeaways:
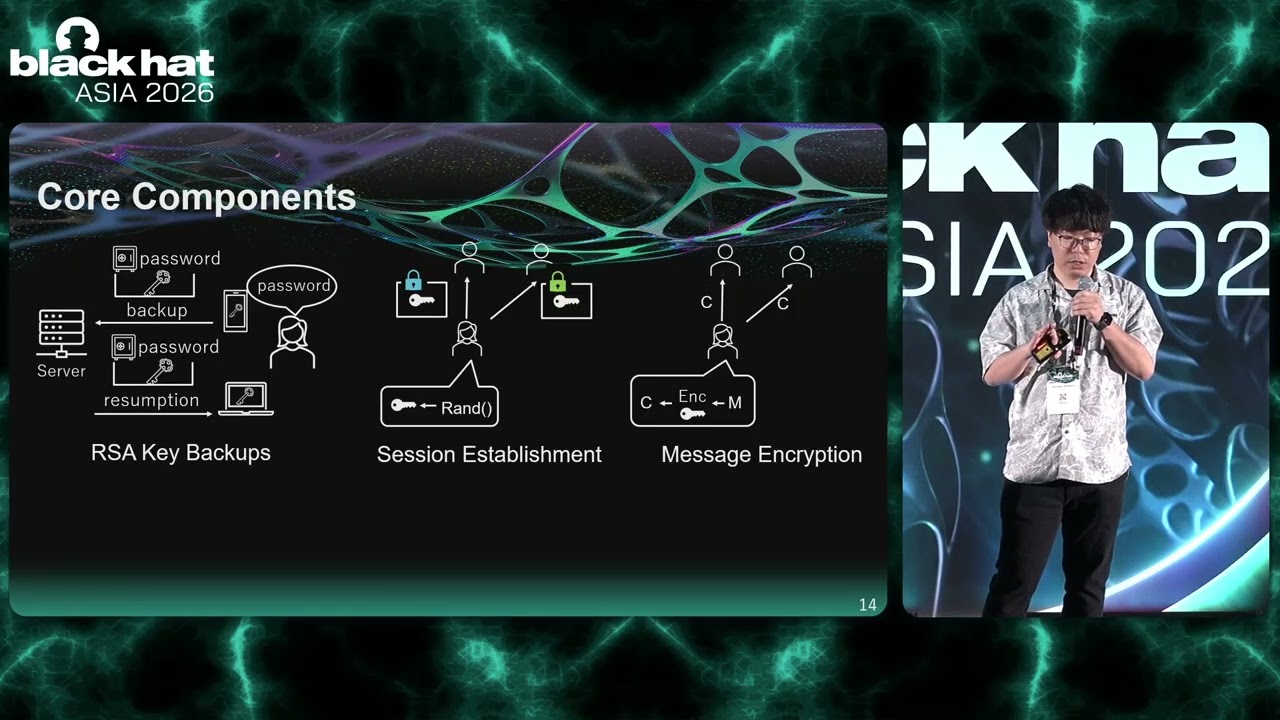
• The E3EE architecture relies on three vulnerable components: RSA key backups, legacy RSA session establishment, and CBC-mode message encryption without integrity checks 2:50.
• The password protecting the private key backup is generated using a non-cryptographic random number generator (Mersenne Twister) and a flawed character set that silently converts uppercase letters to lowercase, drastically reducing entropy 13:00.
• The key derivation function uses only one iteration of PBKDF2, making it highly susceptible to offline brute-force attacks compared to modern standards requiring hundreds of thousands of iterations 12:00.
• Compromising the E3EE password grants full access to the key hierarchy, allowing attackers to read and forge messages because the system lacks forward secrecy and session key rotation 19:00.
• The password reset mechanism fails to rotate session keys, meaning attackers retain access to past messages even after the user changes their password 21:00.
• The vulnerabilities stem from a design prioritizing multi-device support over security, leading to a single point of failure where a weak password protects the entire encryption chain 26:00.
The findings highlight that documented specifications often mask critical implementation flaws, and developers must avoid using simple password-based key derivation for protecting entire key hierarchies in modern secure messaging systems 33:00.
Sources:
- 0:30 Introduction to the complete breakdown of Rocket Chat's end-to-end encryption.
- 2:50 Overview of the three core components of the E3EE architecture.
- 12:00 Discussion on the insufficient iteration count of the key derivation function.
- 13:00 Analysis of the weak random number generator and character set bias.
- 19:00 Explanation of the impact of compromised passwords on message confidentiality.
- 21:00 Description of the flawed password reset mechanism and lack of key rotation.
- 26:00 Investigation into the design motivations behind the fragile encryption implementation.
- 33:00 Final takeaways regarding the gap between documentation and secure implementation.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Thank you for coming to my talk. Um I'm going to talk about the completely breakdown the end to end encryion of rocket chat the one of the widely deployed opensource messaging platform over the 150 countries. The way found recovery attacks um the meaning is every encrypt that messages on the server could be decrypted by the article on server. So let me walk through um how we go there and our journeys. So I'm Hay Kimra from Japan and this is my second talk time to talk of speaking at brackat. So my last talk um was Black Hat USA 2020 2028 five sorry and this talk is joint research with um my co- researchers uh cryptographers from NCT N corporation and the University of Baka and my background is upstac security engineers and now I moved to the cryp applied cryptography researchers so many of…