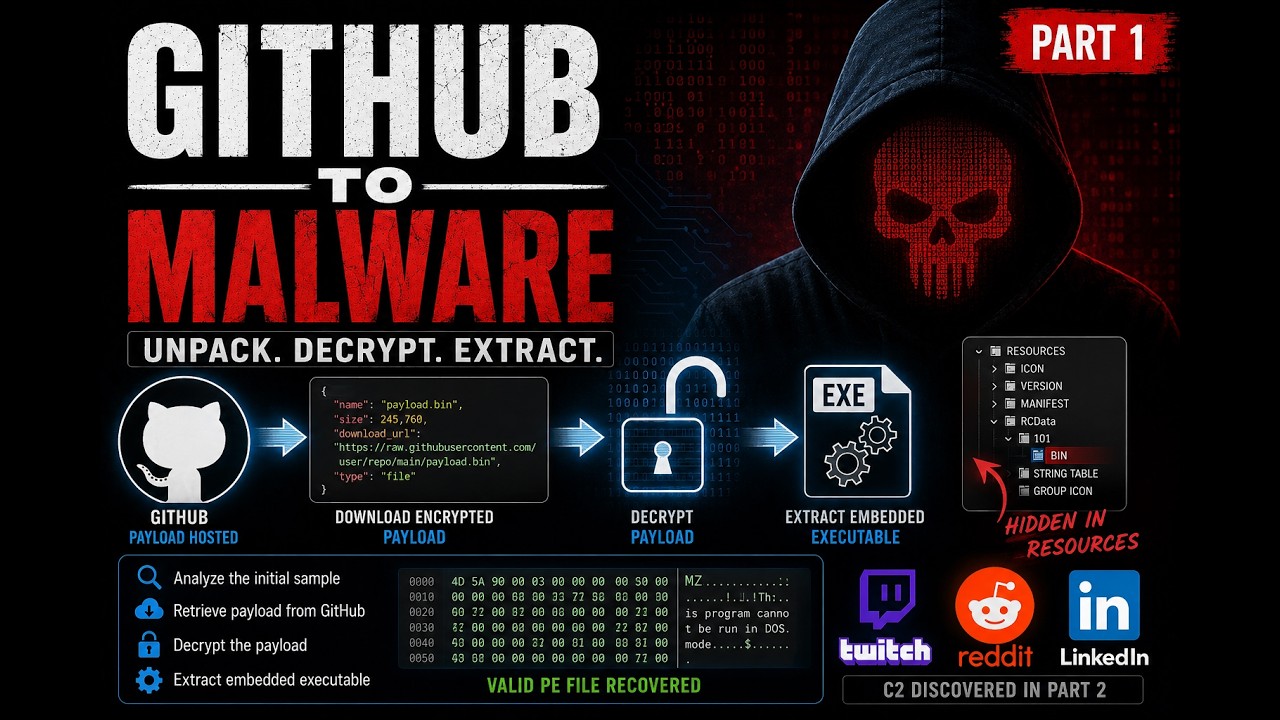
Reverse Engineering a Social Media Malware | GitHub Payload Analysis Part 1
Source: YouTube · Malware Research Diary · published Jun 19, 2026 · 22:25
This video analyzes a recently discovered malicious .NET binary named decrypt_on_dark.exe that communicates with GitHub and Reddit, despite lacking a specific malware name in VirusTotal reports.
Key Takeaways:
• The analyzer found a sample on VirusTotal that reaches out to GitHub and three Reddit links, prompting a deeper investigation into its behavior 0:12.
• The binary is identified as a .NET file obfuscated two months ago and has been flagged as malicious for some time without a specific malware designation 0:43.
• The file name is decrypt_on_dark.exe, with the first submission recorded on March 2nd, and the current analysis is unsigned 0:41.
The video serves as an initial reconnaissance of a suspicious executable, highlighting the importance of investigating binaries that exhibit unexpected network behaviors like contacting social media or code repositories.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Welcome back. Um today let's I found this sample yesterday and I thought it's interesting. So um in the binary I saw that um well in in on virus total I saw that it reach out to you know the the the GitHub which is interesting but there's three witch links in Reddit as well. So um yeah maybe let's take a look and see what it is. So um let's see what is detected as. So the binary name is decrypt on dark decrypt.exe is a net file two month ago offiscated um and it's been detected as a malicious right for some time but there's no specific um um name for it of the mware. So I saw a dark um yeah this uh first submission is in March 2nd and the last is um analysis is this not sign um so yeah let's let's take a look and see um my goal is basically just to see what this does and um um why is reach…