The Certificate Strikes Back: ADCS's Path to Azure | SO-CON 2025
Source: YouTube · SpecterOps · published May 6, 2025 · 38:57
BLUF: This presentation details how attackers can leverage Active Directory Certificate Services (ADCS) to extend certificate abuse into Microsoft Entra ID, facilitating persistent access and identity compromise 0:08.
Key Takeaways:
• The speaker, Fletcher Davis, introduces the topic of extending certificate abuse from on-premises ADCS to cloud-based Entra ID authentication 0:05.
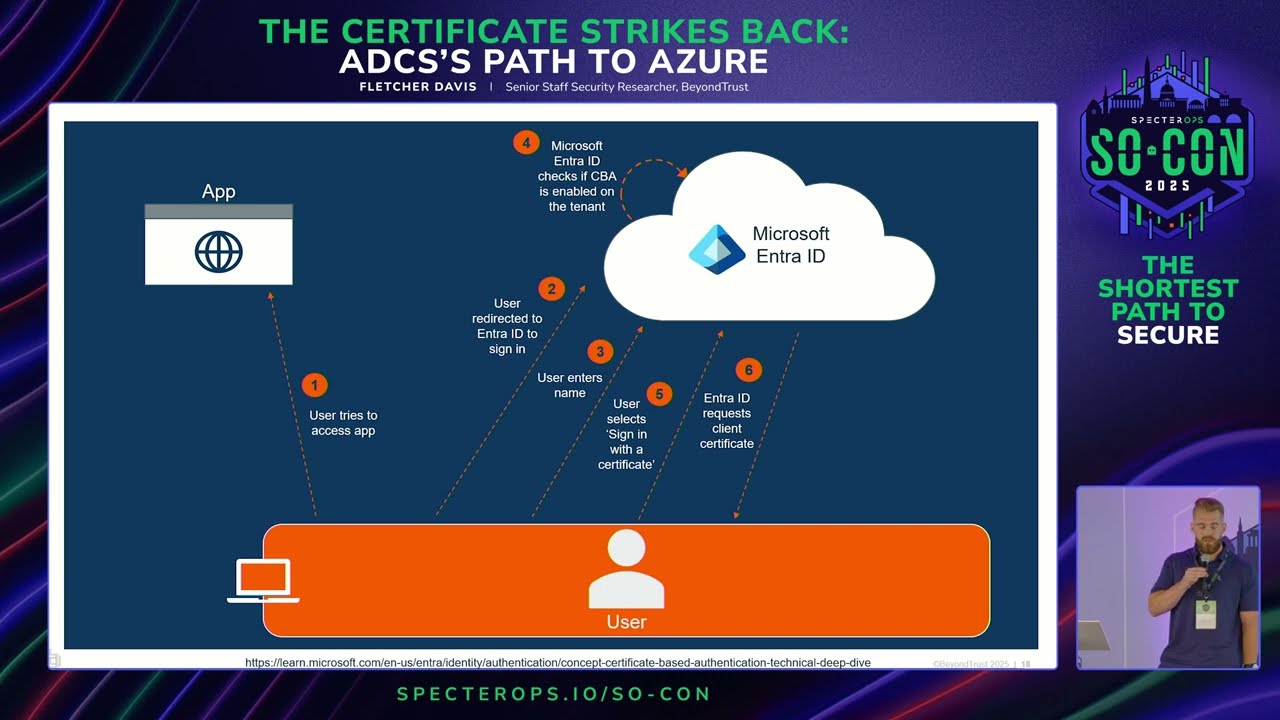
• The technical agenda focuses on explaining the two core components of this attack chain: ADCS and Entra Certificate Based Authentication (CBA) 0:35.
• The discussion covers the foundational technical mechanics that allow these two distinct identity systems to be linked for malicious purposes 0:41.
Closing statement: Understanding the intersection of ADCS and Entra CBA is critical for defending hybrid identity environments against advanced persistent threats.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
[Music] Thank you for having me here today. Uh today's talk is going to be it's called the certificate strikes back. It's how we can kind of leverage things like ADCS to kind of extend the certificate abuse to uh ENTRA. Um my name is Fletcher Davis. I am currently a senior manager of the data science and research team at Beyond Trust. Um before that I come from like an offensive background. I was a principal consultant at CrowdStrike and Mandant. Um and my Twitter handle is Jim Rat. Uh the agenda for today is going to be you know kind of in three phases. I think one going to be the foundational phase kind of explain um you know at a technical level you know the two different components of this attack chain um ADCS and CBA which is entrac or entra certificate based authentication. Um and th…