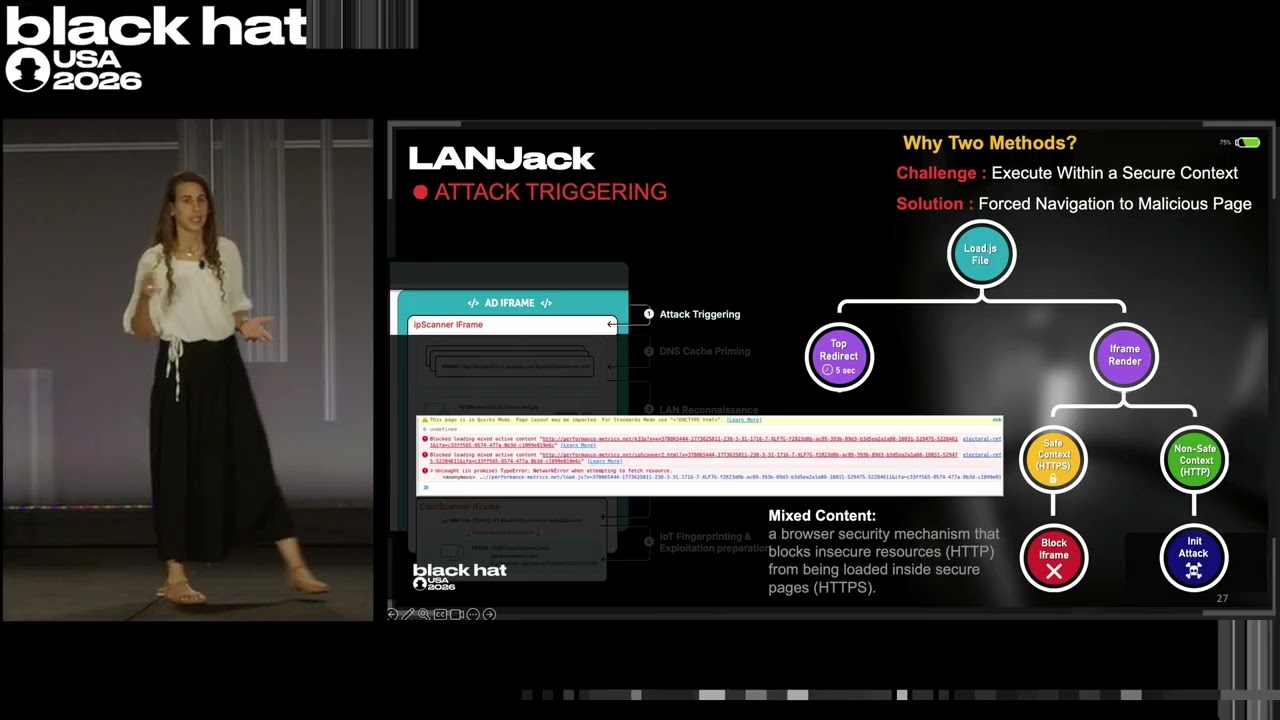
Black Hat USA 2026 | LANJack: Turning Ads into IoT Recon Tools
Source: YouTube · Black Hat · published Nov 16, 2026 · 25:21
This talk unveils "LanJack," the first large-scale malvertising campaign using DNS rebinding to recon IoT devices entirely from the browser—no malware or user interaction needed 5:57.
Key Takeaways:
• Modern ads are executable code served through many intermediaries, making the ad ecosystem a distributed platform for third-party code and supply chain-style attacks 2:25.
• DNS rebinding bypasses the same-origin policy: a domain re-resolves to an internal IP, letting the browser unknowingly interact with internal resources 4:27.
• The campaign was found accidentally: a Coca-Cola-branded ad loaded suspicious "IP scanner" resources over HTTP with thousands of internal-targeting keywords 6:28.
• The five-stage attack uses cloaking, hidden iframes, DNS cache priming, browser timing tricks to find the gateway and scan the subnet, then rebinding plus favicon hashing to extract device details 10:08.
• A variant abused CSP violation reports as a side channel to detect whether victims were logged into Google/Facebook—recon for targeted attacks 20:03.
• The attack combined ad trust, browser quirks, and CSP side channels; assume browser-reachable resources are attacker-reachable and harden IoT authentication 24:23.
Malvertising can deliver fully browser-based attacks against home networks—treat ads as untrusted code and secure IoT devices.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
So, everyone knows that no device is actually safe. And it's going to be because of multiple reasons. But what if I tell you that a simple advertisement, something that we see everywhere on the internet and supposed to be isolated from the internal network, can be the initiator of a breach? That's what this research is about. So, hi everyone. My name is Moria Pedael. When I was a kid, I wanted to be a graphic designer. I was fascinated by the idea of manipulating images. This is an example of a masterpiece from back then, so please don't judge. Now, I couldn't afford the software, so I pretty much downloaded every cracked version I could find on the internet. So, I suppose that was the reason I fell to viruses I we ever had. Now, and now I'm working as a security researcher at GeoEdge, a c…