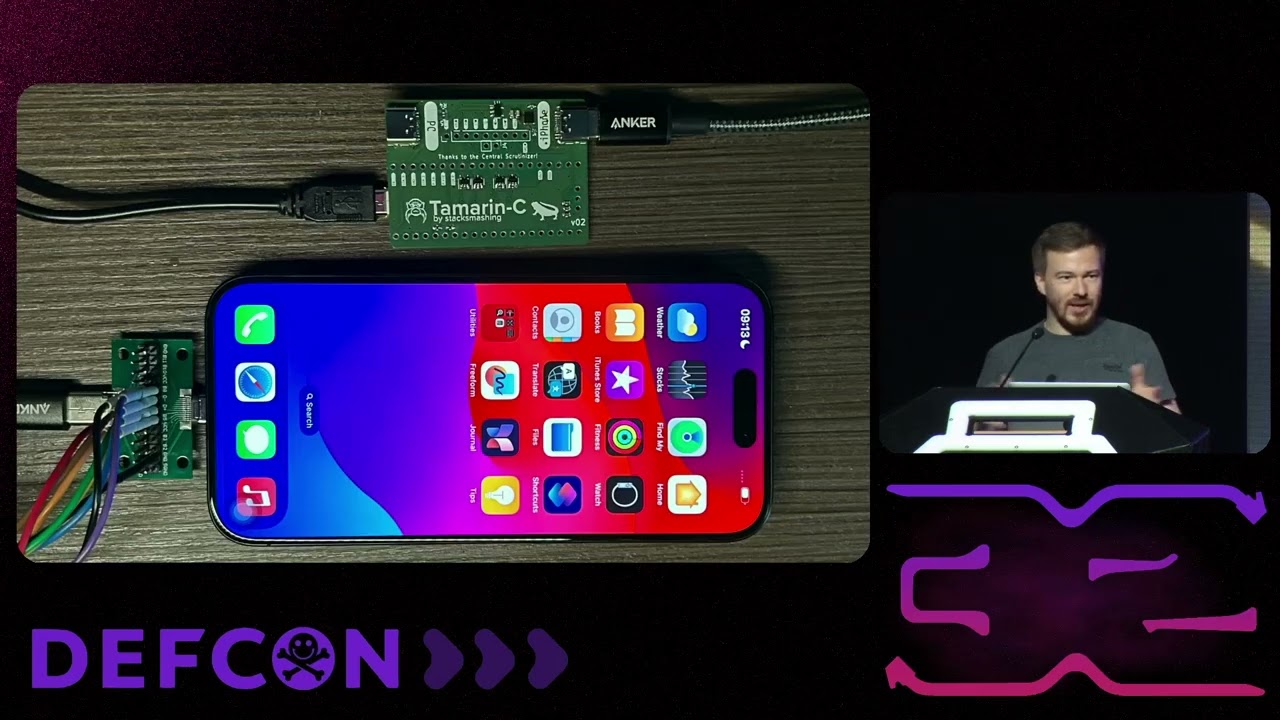
DEF CON 32 - From getting JTAG on the iPhone 15 to hacking Apple's USB-C Controller - Stacksmashing
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 36:56
[BLUF: The speaker demonstrates how to achieve code execution and firmware dumping on Apple’s USB-C Port Controller (Ace3) in the iPhone 15 and MacBook Pro M3 using electromagnetic fault injection, despite the chip’s lack of documentation and secure boot.]
Key Takeaways:
• The Ace3 USB-C controller in Apple devices contains undocumented firmware and debug ports, enabling reverse engineering via vendor-defined messages and JTAG-like access 14:10.
• A vulnerability allows bypassing secure boot by modifying external flash patches, enabling persistent firmware changes even after system restore 15:52.
• Using electromagnetic fault injection, the speaker successfully dumped the Ace3 ROM and RAM by analyzing side-channel EM emissions and timing glitches 28:00.
• A simple memory read payload was built by exploiting a shared USB W command handler between Ace2 and Ace3, enabling arbitrary memory access 34:17.
[This work reveals a path to reverse-engineering undocumented hardware and highlights the potential for persistent attacks on Apple’s USB-C controllers.]
Sources:
- 14:10 Discussion of debug ports, SWD access, and external flash patching in Ace2/Ace3.
- 15:52 Explanation of patchable signature verification and persistent firmware modifications.
- 28:00 Description of electromagnetic fault injection and side-channel timing analysis.
- 34:17 Demonstration of memory read exploit using shared USB W command handler.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
hey everyone welcome to my talk asce of the sleeve hacking into Apple's new USBC controller uh first off who am I my name is Thomas Roth AKA stack smashing I'm a security researcher for hardware and firmware and I'm also a co-founder at this online training platform called hex.io you can find me on Twitter Youtube and so on now as always like any research is built on top of other people's work right and so I want to thank for example siga uh who built a colel module we will use uh Olive for the Thunderbolt Patcher the aahi Linux Team without whose reverse engineering work I couldn't do anything Car Mar who just always was there when I talked and had to rent about fault injection Yar Fabian andaro Mark Z for the Central scrutinizer and also the t812 de team who did some awesome work now a b…