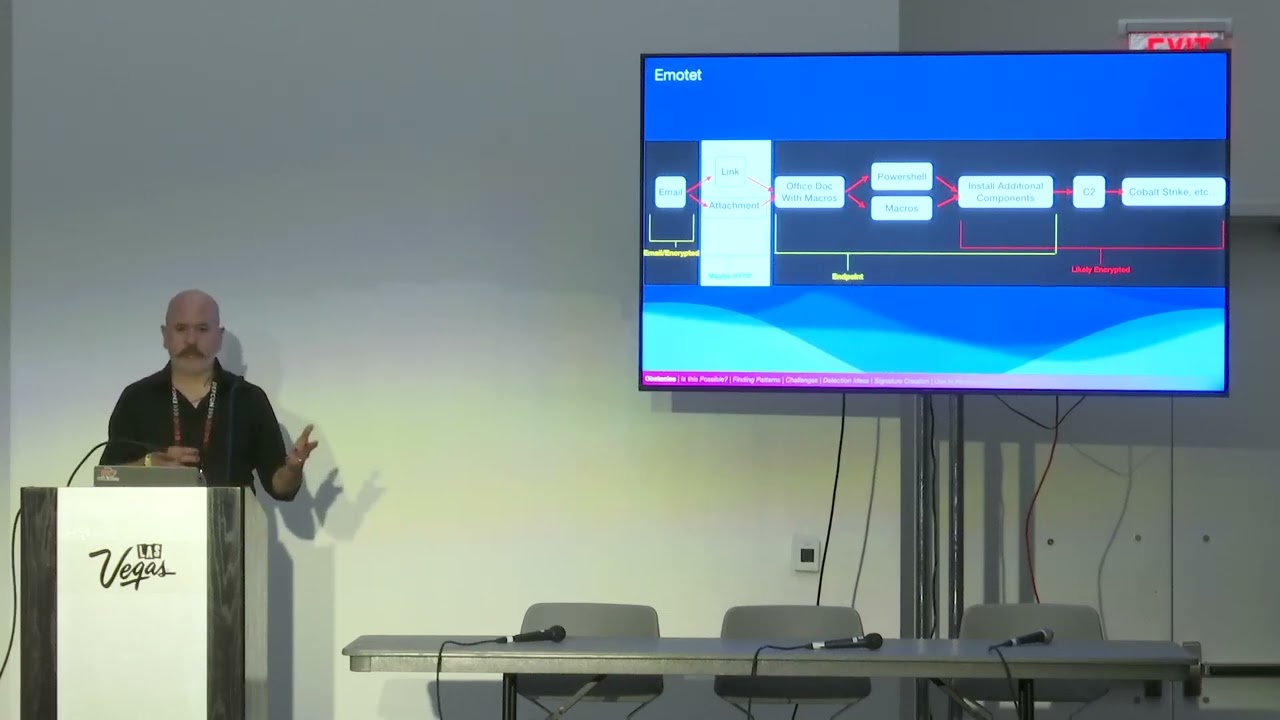
DEF CON 32 - Signature-Based Detection Using Network Timing - Josh Pyorre
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 42:44
The speaker develops a method to detect and attribute malicious network activity by analyzing time patterns in malware traffic, using techniques like average time intervals, co-integration, and Levenshtein distance to identify behavioral similarities between malware samples, even when they differ in surface-level details. This enables detection of new or evolving threats without requiring full signature matching.
Key Takeaways:
• Attribution and infection chain analysis using malware samples from sources like VirusTotal and any.run, tracking URLs and hashes to map threat actor behaviors 2:00-2:49
• Detection of malicious traffic via network packet analysis, using YARA rules to identify specific post content, user agents, and referrers in HTTP traffic 6:24-7:00
• Use of time-based patterns—average intervals between transactions and timing differences—to distinguish between benign and malicious flows, even across different malware variants 11:00-15:00
• Application of co-integration and Levenshtein distance to compare time-series data from network flows, identifying behavioral similarities between malware campaigns despite differences in execution 16:10-25:00
• Development of a signature-based detection system that converts network transaction timing into audio patterns, enabling potential pattern recognition via tools like Shazam, though currently impractical for production use 35:00-39:00
This research-driven approach leverages behavioral analysis and time-series patterns to detect threats, offering a flexible alternative to traditional signature-based detection.
Sources:
- 2:00-2:49 Attribution and infection chain m
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
all right good afternoon everyone and it is 1:30 uh Pacific time in beautiful Las Vegas Nevada um thank you so much for joining us today and this next talk is um sponsored by the packet hacking Village and it is my absolute pleasure to introduce to you Josh porori thank you all right so that's me I uh work with SEC Cisco Talos um previously I've worked with zscaler um umbrella Open DNS NASA and Mand and some other places some nonprofits and whatnot so I do security research and I uh make music and do a bunch of other stuff so uh before I get into all the details I'm going to talk about what I want to focus on when I'm doing this kind of thing I'm going to talk about attribution and the infection chain real quick and uh it's probably very familiar to you so hopefully I'm not going to bore e…