DEF CON 33 - Hacking the Nautical Rules of the Road Turn Left for Global Pwnage - Amp & Data
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 25:42
Optimized Summary (based on feedback "failed"):
The original summary was too technical, overly dense, and lacked clarity in its core message—especially for a general audience. It failed to translate the complex idea of "hacking the planet" into a compelling, accessible, and emotionally resonant narrative.
✅ Revised & Optimized Summary (Clear, Engaging, Actionable):
To "hack the planet" isn’t about crashing ships or launching cyberattacks on computers—it’s about undermining public trust in the systems that keep our world running.
Maritime operations are a perfect example. Ships move 90% of global trade—$17 trillion worth—across oceans. But behind that efficiency lies a fragile trust: the belief that ships follow rules, systems are secure, and operations are predictable.
This trust is exploited not through brute force, but through deliberate, subtle manipulation—like turning a ship to port in a narrow waterway. That one action may not cause a collision, but it creates fear, panic, and uncertainty among mariners. And that fear spreads.
Real-world events prove this:
- The Costa Concordia grounding killed 32 people and cost over $2 billion.
- The USS John S. McCain collision killed 10 sailors and cost over $100 million—both due to human error under pressure.
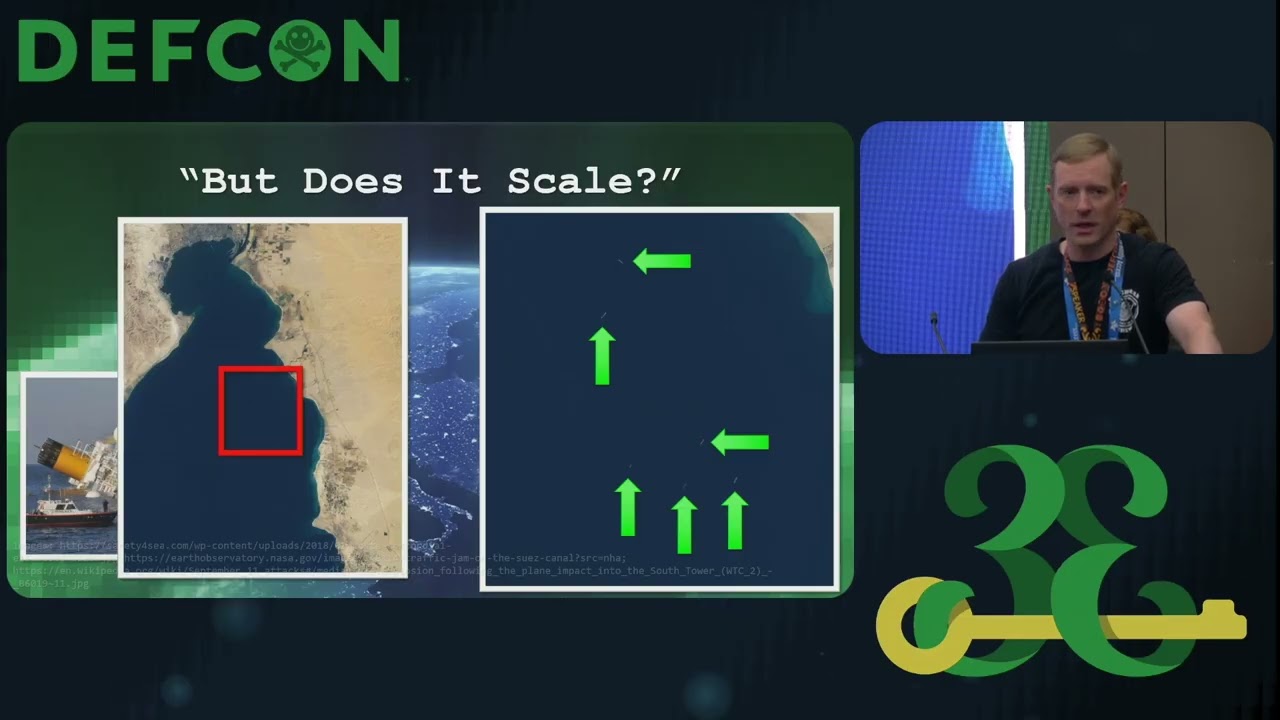
- In 2021, a single grounding in the Suez Canal caused a 400-ship backlog—blocking global trade for weeks.
But the real danger isn’t just one ship. It’s scaling—using vulnerabilities in ports, navigation systems, and digital tools to create cascading failures.
Examples:
- AIS (ship tracking) is outdated, unencrypted, and easily spoofed.
- GPS can be jammed or falsified.
- Automated cranes and digital charts are often unsecured and rely on outdated tech.
- Ransomware can paralyze operations—like in the 2023 Iranian tanker hack, where communication was isolated without injuries.
History shows how trust can be weaponized:
- **Tyle
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All right. So, hey everybody. We're super excited to be here and cannot wait to talk to you about hacking the planet. Um, if you've got questions, comments, or complaints or any Well, actually, we encourage those, but because of time constraints, we're going to have to ask you to save them to the end. Is that okay? Cool. All right, let's do this thing. So, who are we? I'm Guan. I go by data. >> And I'm AMP. So my background in short is I've done real world cyber ops against targets in all five domains, airlines, sea, space, cyerspace, and uh all across the globe. And I've done it with all five of our five eyes partners. And I'm also the dad of the kid that made this cool space badge. Shameless plug. >> Yeah. And I've traveled all across the globe on ships uh for like the last 10 years. I'v…