DEF CON 34 - Main - Breaking the Ethereum Phone From BootROM to Wallet Signing Keys - Guanxing Wen
Source: YouTube · DEFCONConference · published Nov 6, 2026 · 23:53
A security researcher reverse engineered the Ethereum Phone (cryptophone), showing its unsecured MediaTek download mode enabled full boot chain compromise, private key theft, and airdrop theft 2:15.
Key Takeaways:
• Cryptophones aim to solve the wallet trade-off (browser wallets easy but insecure; hardware wallets secure but cumbersome) by protecting keys in an enclave on a smartphone 1:03
• Android keystores only support secp256r1 (not Ethereum's secp256k1), requiring custom trusted execution, which prompted reverse engineering 2:30
• Unblown SLA/DA flags in download mode allowed uploading a patched preloader for early boot access 4:54
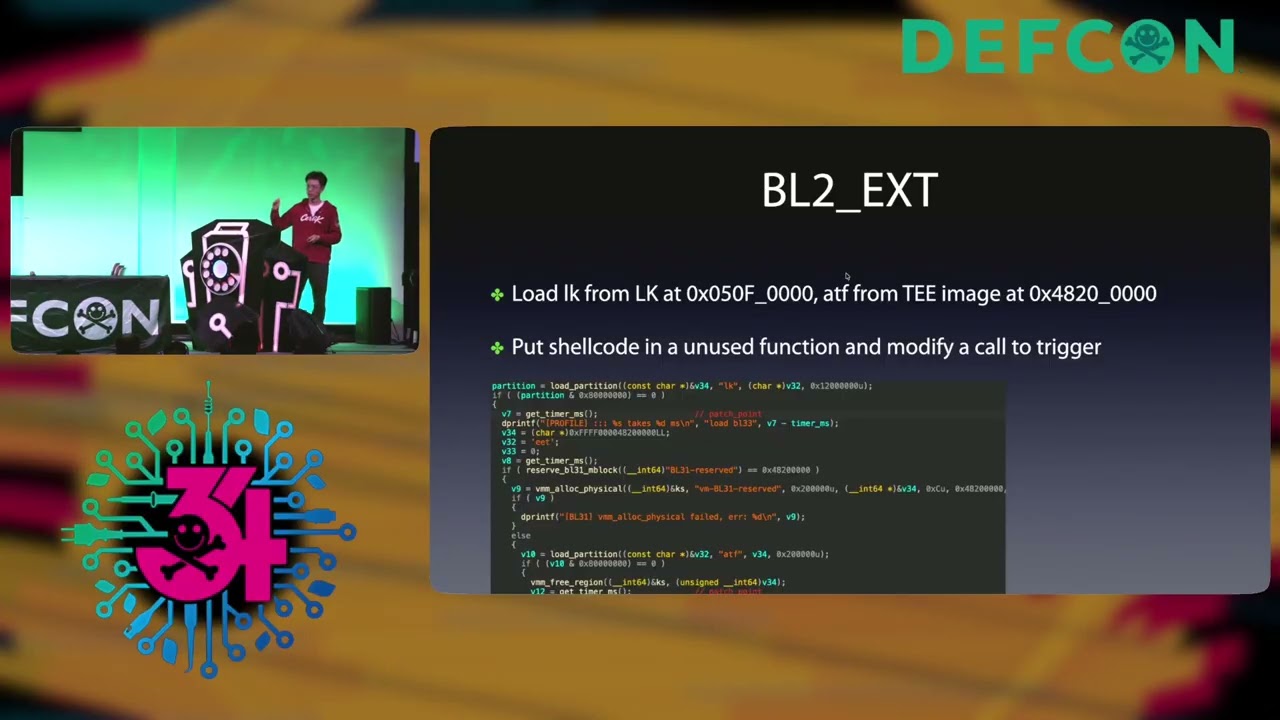
• A "load of loader" technique chains shellcode through each boot stage, bypassing signature verification in memory until the kernel 6:30
• Screen lock uses only a soft gatekeeper in userland, enabling offline PIN brute force in under 10 minutes 17:31
• Private keys are stored unencrypted; the extracted key was verified on-chain to control the wallet on Base 19:26
• Airdrop eligibility uses an IMEI + serial hash printed on the retail box, enabling "minus one click" theft before delivery 22:14
Cryptophones inherit weaknesses from both smartphone supply chains and blockchain systems, with airdrop incentives turning hardware flaws into direct financial theft.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Uh so nice to be here and we're competing the keynote right now. So I'm very impressed that you're here. Uh so today I'm going to talk about uh the Ethereum phone. Um so and use it as a case study uh of the emerging device category called cryptophone. And so first something about myself. My name is Gwen Singen and I'm currently researcher atic. So my most interest topics are lower level systems like foot loader and trust zone. And recent years I move forward to the intersection between the uh traditional security infrastructure and blockchain systems. So the cryptohone became a very interesting target to me because they're not just smartphone, they're not just hardware wallet. Uh what happened? I should plug in. Okay, so the crypto phone is very interesting to me. Uh typically if you want …