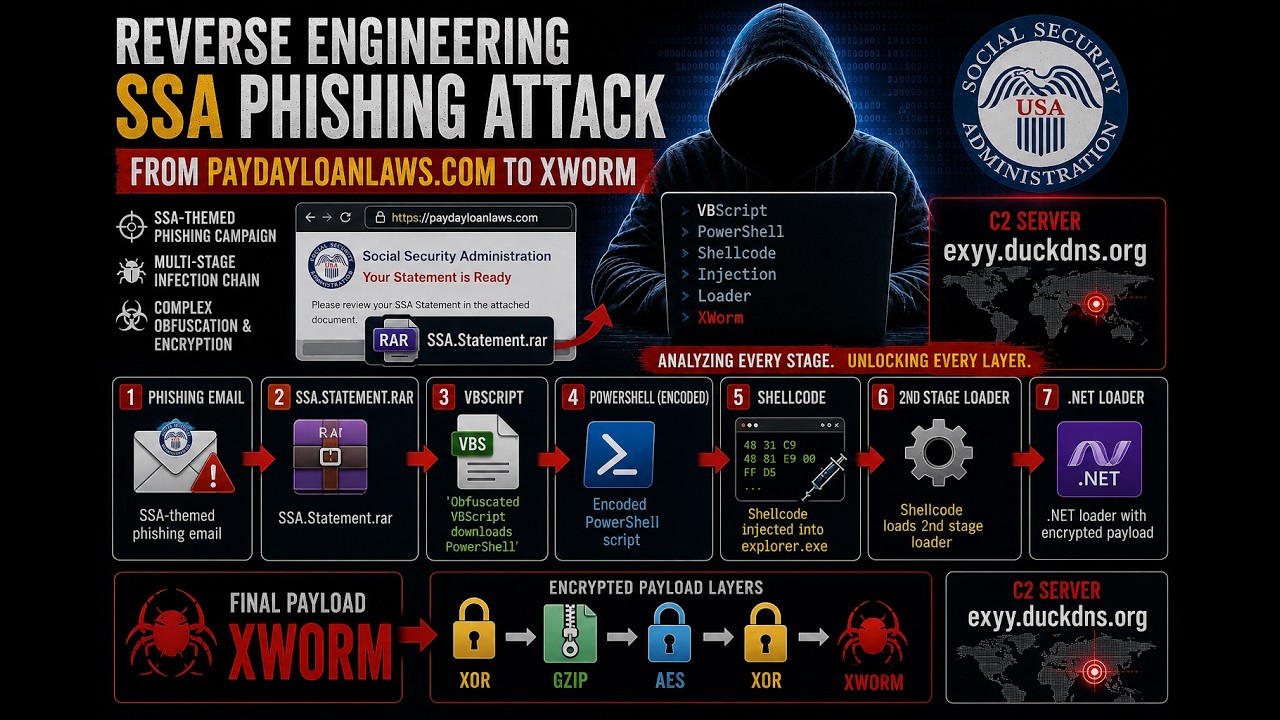
Reverse Engineering an SSA Phishing Attack | VBScript → PowerShell → Shellcode → XWorm
Source: YouTube · Malware Research Diary · published Sep 1, 2026 · 52:38
[BLUF]
This video details the analysis of a sophisticated social security-themed phishing campaign that deploys a multi-layered malware loader, ultimately delivering the XClient infostealer, rather than the typical ScreenConnect or OMI remote access tools 0:41.
Key Takeaways:
• The campaign utilizes a domain mimicking payday loans to target lawyers or the elderly, leveraging a Telegram token for victim data callback 1:12.
• Initial infection involves a small payload that drops an encrypted PowerShell script, which then downloads and executes a secondary stage in memory 3:38.
• The secondary stage employs shellcode injection into explorer.exe and establishes persistence via a scheduled task named "Windows Driver Helper" 6:01.
• Analysis reveals a complex decryption scheme using AES and GZip compression within a .NET assembly to hide the final payload 39:00.
• The final delivered payload is identified as XClient, an infostealer and clipboard hijacker, with configuration parameters including mutex names and C2 settings 45:51.
The analysis highlights a deviation from standard cybercriminal tactics, suggesting a more advanced or APT-like approach due to the heavy obfuscation and multi-stage deployment.
Sources:
- 0:41 Introduction to the non-typical social security phishing kit.
- 1:12 Analysis of the phishing domain and target audience.
- 3:38 Execution of the encrypted PowerShell payload.
- 6:01 Shellcode injection and persistence mechanisms.
- 39:00 Decryption logic using AES and GZip in the .NET stage.
- 45:51 Identification of the final XClient infostealer payload.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Welcome back to the another session in analyzing malares. Um today let's um let's go over some social security um theme type of fishing um website. So um yesterday I found this um it's offline right now but um basically using social security theme to drop a payload. Um typically we seen um most of the um fishing kit using this type of theme to deploy like screen connect type of OMI type of software. Um but in this case it's slightly different. So um let's take a look and walk through the whole um process. I did initially um analyze um a little bit of it um before I stop. So let's let's walk through it. So I'm I'm basically um going through the um the data through the um URL scans.io and the website is payday loan.law. laws.com. So likely they target um lawyer um or you um e…