DEF CON 33 - CTRAPS-CTAP Impersonation, API Confusion Attacks on FIDO2 - M Casagrande, D Antonioli
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 37:25
Revised Summary
CITRUPS: Client Impersonation and API Confusion Attacks on FIDO2
Researchers Marco and Daniel have identified eight critical design vulnerabilities in the FIDO2 setup protocol, enabling severe attacks that compromise authentication systems across major services including Apple, Microsoft, and Google.
Key Findings
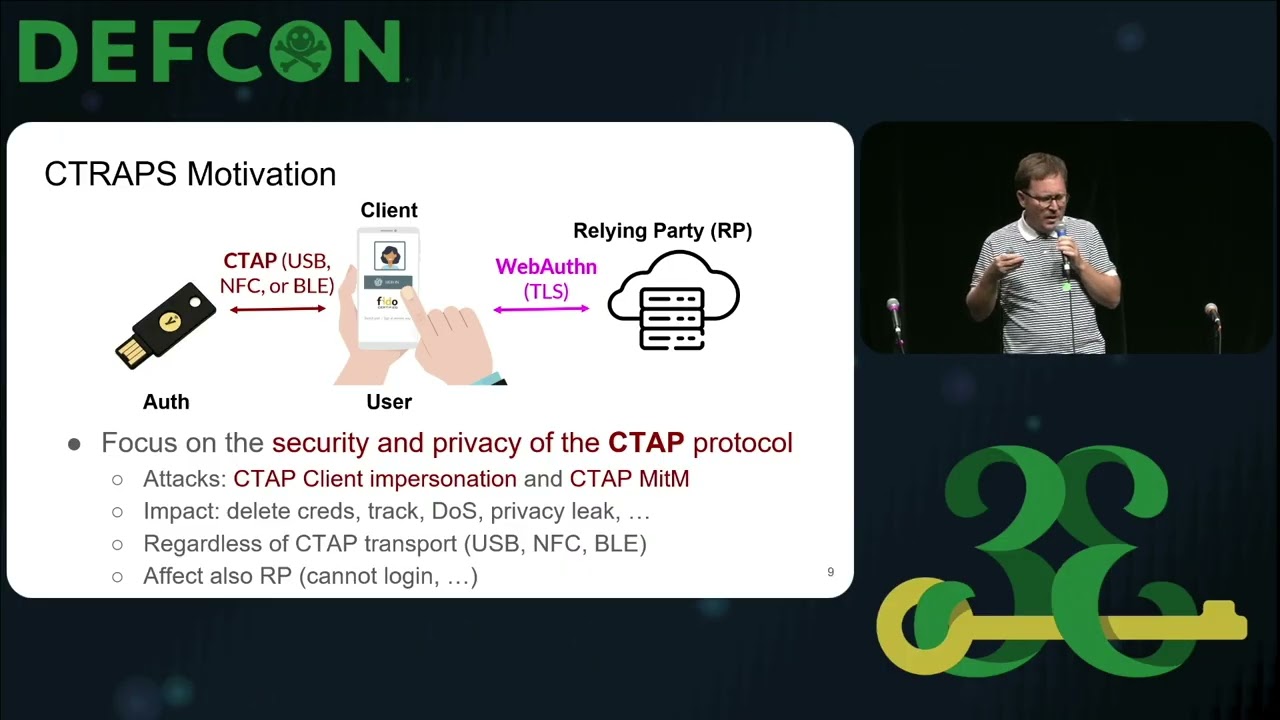
Protocol Vulnerabilities: The researchers discovered eight critical design flaws in the CTAP (Client to Authenticator Protocol) portion of FIDO2, including lack of authentication, no feedback on API calls, and insufficient user presence checks.
Attack Categories: They demonstrated 11 distinct attacks:
- 4 client impersonation attacks: Where an attacker poses as a legitimate client to perform unauthorized actions
- 7 API confusion man-in-the-middle attacks: Where attackers manipulate API calls to execute unauthorized operations
Real-World Impact
- Authentication Compromise: Attackers can factory reset authenticators, delete user credentials, track users via unique identifiers, and deny service to legitimate users.
- Widespread Vulnerability: The attacks successfully compromised 6 popular authenticators (including Ubico, Google) and 10 major relying parties (Apple, Microsoft, Nvidia, etc.).
- Serious Consequences: Affected users risk complete loss of credentials, unauthorized tracking, and inability to access critical services.
Research Tools and Methods
The team developed and released an open-source toolkit featuring:
- Virtual testbeds for safe vulnerability testing
- Attack clients for Android and Electron platforms
- Tools that work across multiple transport layers (USB, NFC, Bluetooth)
Disclosure and Response
The findings were responsibly disclosed to the FIDO Alliance in November 2023 and to affected vendors including Ubico and Google. While some newer models have received fixes and CVEs, many older authenticators remain vulnerable.
The research underscores the urgent need
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. I'm Marco and uh today we will be uh presenting Citrups Citup client impersonation and API confusion on Pho 2. So I'm Marco. I'm a postto at KTH in Sweden. Uh I've done this work while I was doing my PhD at UROM in France under professor Antonio which will talk uh with me as a co-speaker. My research is in security and privacy. So I look at uh proprietary and standard protocols of IoT devices for example uh authenticators from 5.2. I also look at mobile so Android and transport very common ones like Bluetooth energy, Wi-Fi, NFC and so on. So now um Dan will have the uh stage for him. All right guys, uh thank you for coming to our talk. Uh my name is Daniel Antonioi. I'm an assistant professor at Turkom, a university and research center located in Sophianis in southern part …