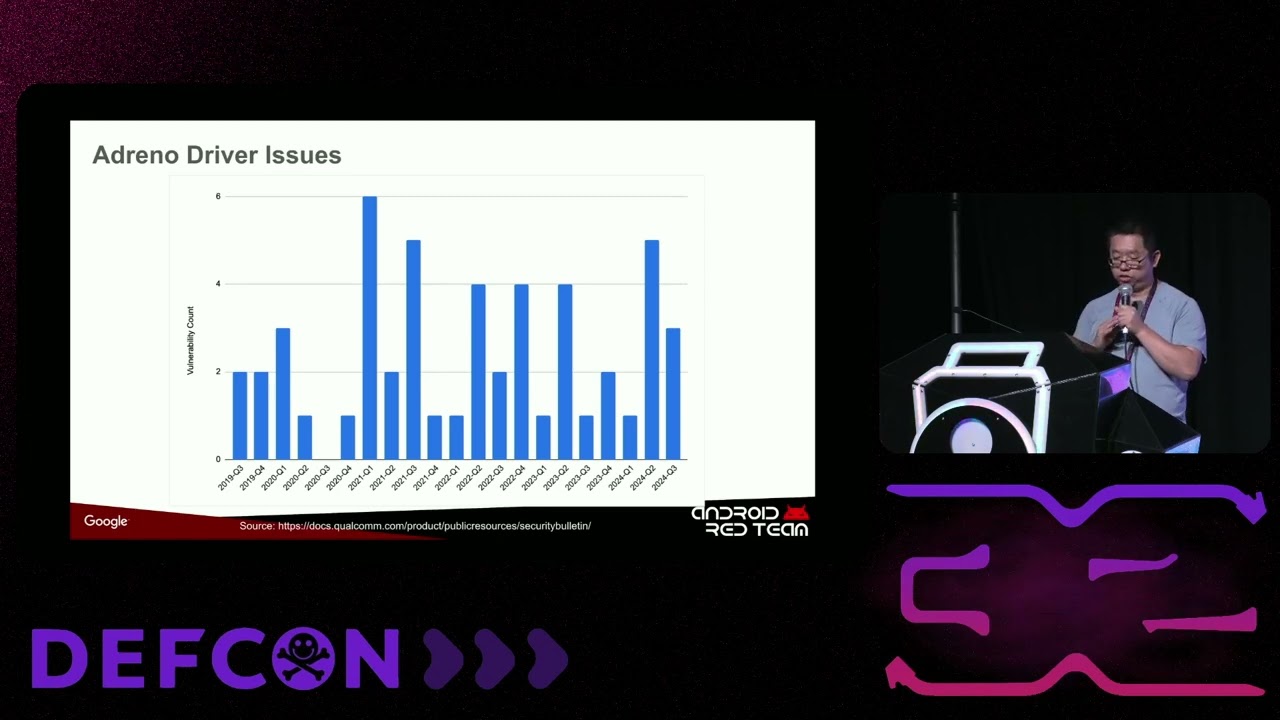
DEF CON 32 - The Way To Android Root: Exploiting Smartphone GPU - Xiling Gong, Eugene Rodionov
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 46:18
This presentation demonstrates how the Android Red Team discovered and exploited CVE-2024-23380, a vulnerability in Qualcomm Adreno GPU drivers that allowed them to gain root privileges on Android devices 9:35-9:57.
Key Takeaways:
• GPU drivers are attractive attack targets because applications don't need special permissions to access them, providing a direct attack surface to untrusted code 1:19-2:14
• The vulnerability was a race condition in the virtual buffer object (VBO) binding process where physical-to-virtual mapping occurred outside of a protected lock section 19:13-19:23
• By triggering the race condition with two threads (one binding, one unbinding), they could create a use-after-free condition allowing access to freed physical pages 21:04-21:26
• The exploit involved spraying kernel memory with specially crafted structures, modifying physical addresses to point to kernel memory, and mapping the entire kernel to user space 30:26-31:23
• The team demonstrated the exploit on a smartphone with Snapdragon Generation 8, successfully gaining root access 39:17-39:23
The team discovered this vulnerability through manual code review and patch analysis, suggesting that moving GPU processing to an out-of-process model and using memory-safe languages could improve Android security.
Sources:
- 1:19-2:14 Explanation of why GPU drivers are attractive security targets
- 19:13-19:23 Technical details of the VBO binding vulnerability
- 21:04-21:26 Explanation of the race condition tri
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
okay okay sorry for that um good afternoon everyone my name is shin I'm the manager of Android red team today uh today I'm really uh honored to present you the way to Android route exploiting your GPU on smartphone with these two gentlemen uh this is shiling our security researcher and uh he actually did most of the work uh technical work so big gr credit to him and also next to shilan is our Tech lead Eugene Rod nor Eugene did a lot of work to help us creating the slid and making sure demo run smoothly big shout out to him so our story dated back to the early this year when sheiling decided to take a look at forom GPU drivers um but before we go into detail here's the brief introduction of our team so we are the Android red team our goal is to increase the Android and pixel security and w…