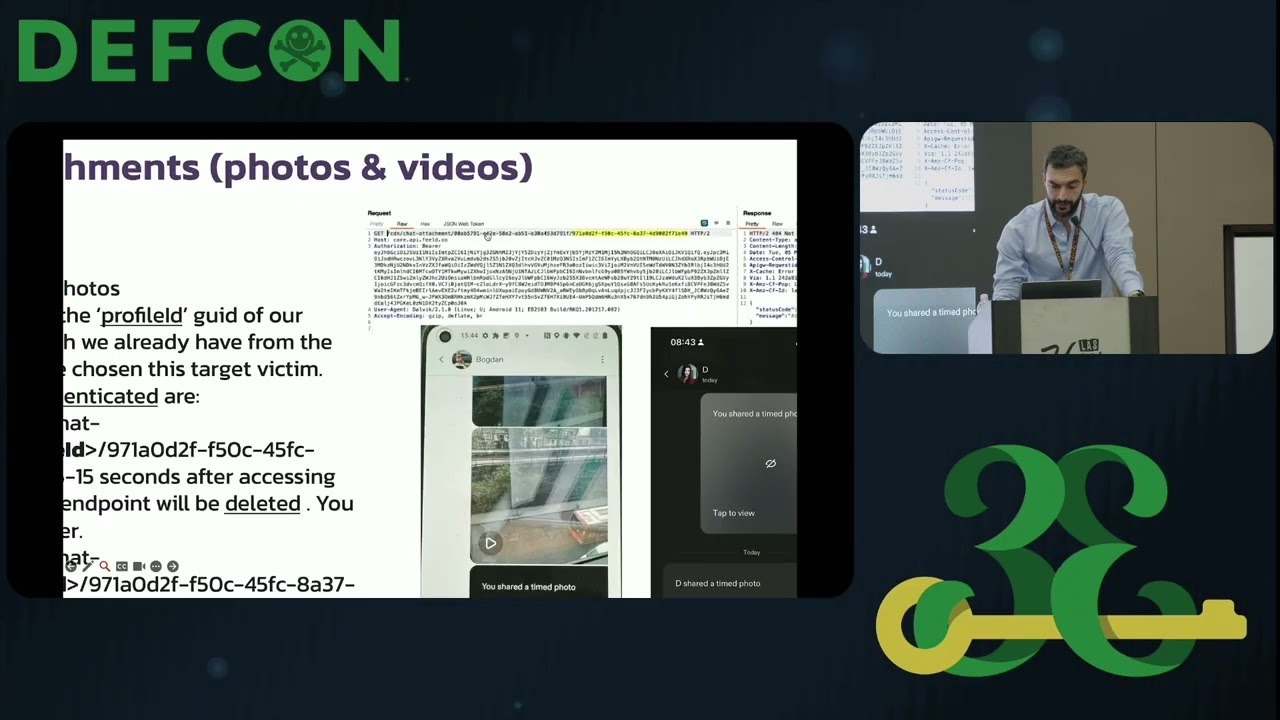
DEF CON 33 - Examining Access Control Vulnerabilities in GraphQL: A Feeld Case Study - Bogdan Tiron
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 25:21
The presenter demonstrates critical access control vulnerabilities 0:00 in the Feeld dating app, exposing how broken object level authorization (BOLA) flaws can lead to severe data exposure 0:53.
Key Takeaways:
• Non-premium users could bypass paywalls and access profile information meant for premium subscribers by intercepting GraphQL requests 5:15
• Attackers could access all user attachments including photos and videos, even those marked as time-limited or "view once," which remained publicly accessible 10:00
• Eight distinct access control vulnerabilities allowed unauthorized actions including reading messages, deleting/editing content, updating profiles, and impersonating users 3:00
All reported vulnerabilities were patched after 6 months 23:35.
Sources:
- 0:00 Introduction to access control vulnerabilities
- 0:53 Explanation of BOLA as top API vulnerability
- 3:00 Overview of 8 discovered vulnerabilities
- 5:15 Profile information disclosure to non-premium users
- 10:00 Accessing user attachments and media files
- 23:35 Vulnerability disclosure and remediation timeline
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
So today we'll be talking about examining access control vulnerabilities in graphical and rest API as well and this will be a case a field case study on data exposure. So we'll be talking about this uh dating app called field field and how the access controls in the rest API and graphical API impacted this app. So who am I? Uh senior pentest for brbridge accredititations in pentesting dev sec ops and GCP security and I've been working in the past in the banking and gambling industry uh especially I have more than 10 years of experience in security especially pentesting. So what is this talk about? This talk is about the importance of access controls and according to our top 10 API um it is on the first place known as uh bola category broken object level authorization and for web a web apps…