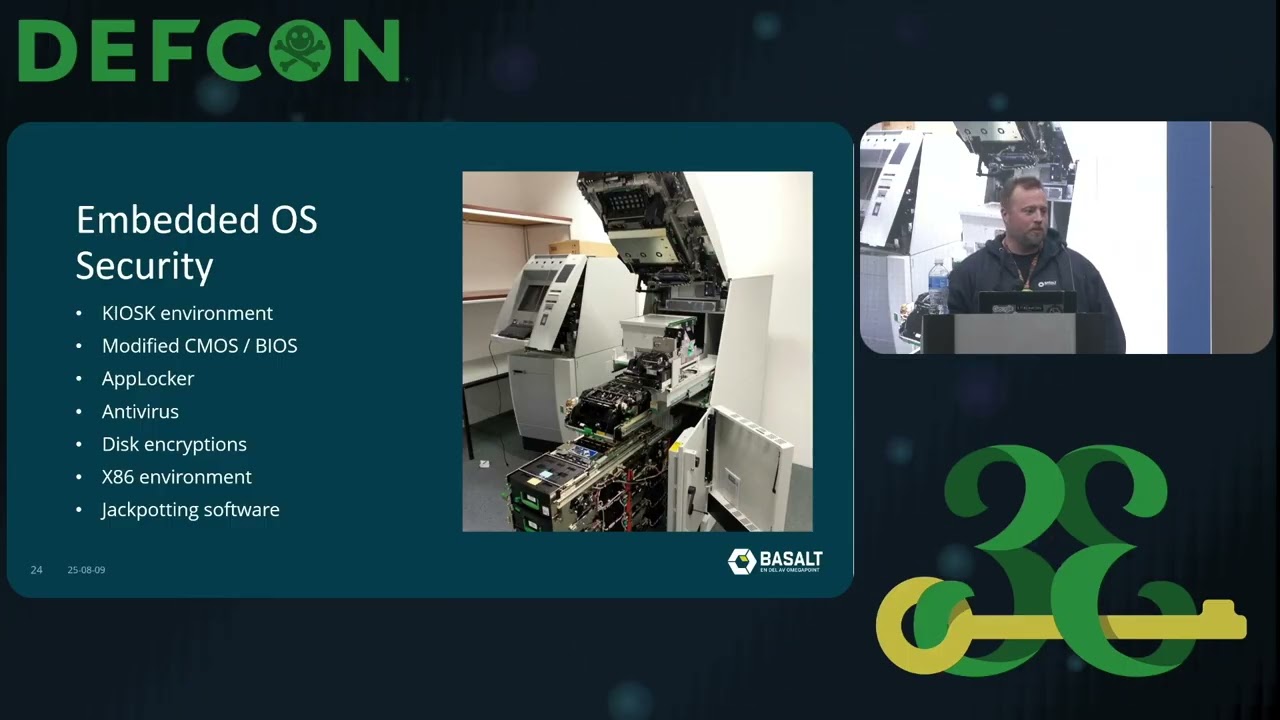
DEF CON 33 - Take all my money – penetrating ATMs - Fredrik Sandstom
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 24:02
The video explores ATM security flaws, emphasizing that many ATMs remain vulnerable due to poor encryption and lack of mutual authentication, enabling hackers to extract cash via simple physical access or network manipulation. A key takeaway is that over 30–40% of ATMs lack disk encryption, making them easy targets for jackpotting software.
Key Takeaways:
• Physical access is often easier than technical attacks; thin metal tops can be breached with tools like shishels or crowbars 17:36–17:55.
• Most ATMs lack mutual authentication between cash dispenser and PC, allowing attackers to connect a USB extension cable and dispense cash without touching the PC 18:06–18:20.
• Many ATMs use unencrypted, home-router-style network gear, exposing transaction logs and camera feeds to attackers 13:00–13:25.
• A real-world heist in Sweden involved two non-technical criminals who used basic tools and exploited missing authentication to extract ~$160,000 in cash 17:02–17:30.
• Banks often prioritize insurance over security, leading to delayed patches and continued vulnerabilities 20:17–20:34.
Attackers can bypass security by exploiting poor physical design, unencrypted networks, and weak authentication—making ATM hacking a persistent, real-world threat despite vendor standardization efforts.
Sources:
- 17:36–17:55 Physical access methods like shishels and crowbars are common and effective.
- 18:06–18:20 Lack of mutual authentication allows USB-based cash dispensing without PC access.
- 13:00–13:25 Unsecured
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
So thank you for coming today. So nice to see a nice turnout. So today's talk basically go through basic ATMs and we go through some war stories of my experience hacking them and some common faults and we finish it off with some uh oh it's it's okay I can and we're finishing off with a small heist from Sweden I got my hands on to just wrap it together with your new skills. So am I. I'm done pen testing for the last 10 years mostly offensive security and I really like ATM hacking because it's the whole field from the physical to kios breakout to everything. So let's jump into it. 30 minutes and a lot to cover. So there are many ways to do this. I mean if you're not technical there are you can always be a forklift operator. Just take it home and do what you need in peace. Maybe in the garage…