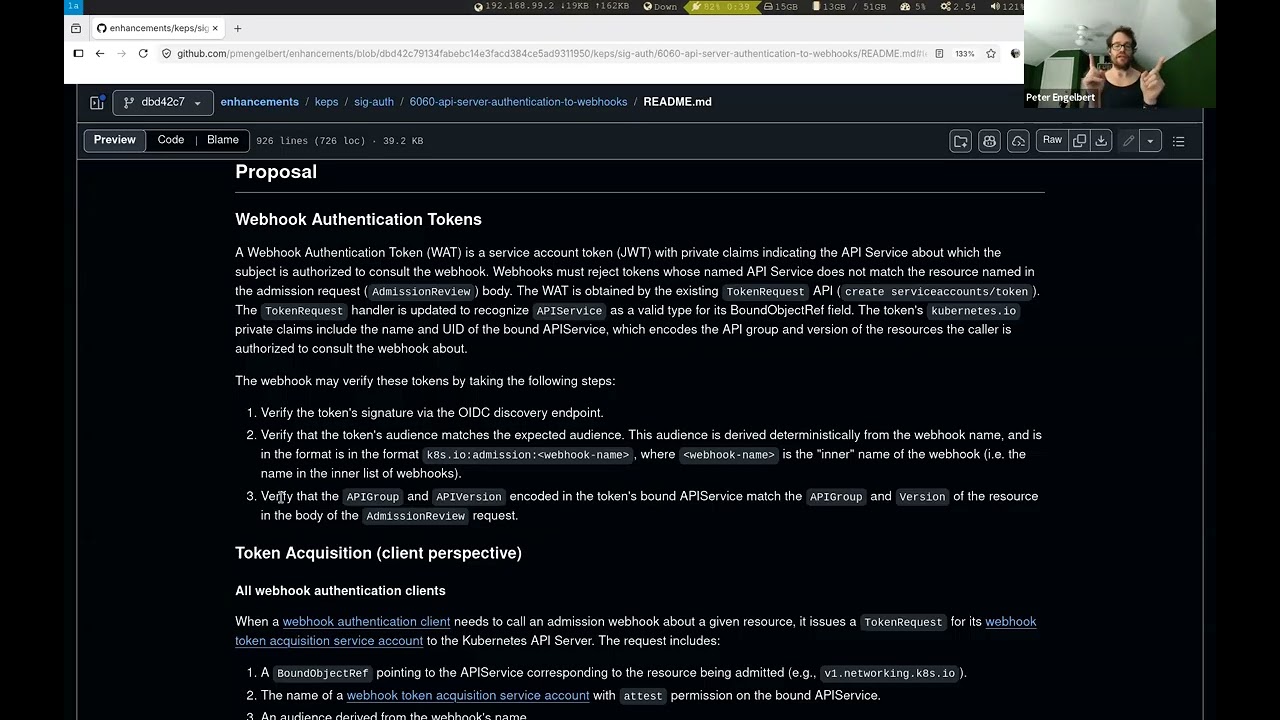
[SIG-Auth] Bi-weekly meeting for 2026-06-18
Source: YouTube · Kubernetes · published Jun 18, 2026 · 24:08
The video explains the default behavior of API servers regarding webhook authentication, highlighting security concerns with admission webhooks that are dynamically configured at runtime.
Key Takeaways:
• API servers do not authenticate themselves to webhooks by default 0:31-0:45
• Admission webhooks pose a particular security challenge as they are dynamically configured at runtime 0:49-0:57
• Authorization, authentication, and audit webhooks require API server restarts to change configuration 1:00-1:13
This technical discussion highlights important security considerations for Kubernetes webhook configurations, particularly around dynamic admission controllers.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cloud Security. Commonly maps to: Security Architecture and Engineering, Communication and Network Security. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Um so we we went over the motivation here some. Um is there anything unclear about why we're doing this? >> No. Okay. For the purpose of the recording, tell us what you're talking about. >> Yep, start fresh. Um So today uh there's by default uh the API server and aggregated API servers will not uh attempt to authenticate themselves uh to webhooks. Um >> [snorts] >> and in particular admission webhooks are a problem because they are dynamically configured at runtime, whereas authorization, authentication, audit webhooks are not. Um and so often um and and those aren't dynamic and require an API server restart to change anyway. Um So and in that case, the person setting up the webhook is usually the same person setting up the API server so that they can be coordinated uh on the authenticatio…