Black Hat USA 2026 | Breaking Multi-Tenancy Over and Over, and What We Can Learn From This
Source: YouTube · Black Hat · published Nov 20, 2026 · 37:21
BLUF: Industry best practices like network policies are insufficient for securing Kubernetes multi-tenancy, as researchers demonstrated how insecure cross-namespace references in Kubernetes CRDs and annotations allow attackers to bypass isolation, steal credentials, and escalate to cluster admin rights 2:01-2:18.
Key Takeaways:
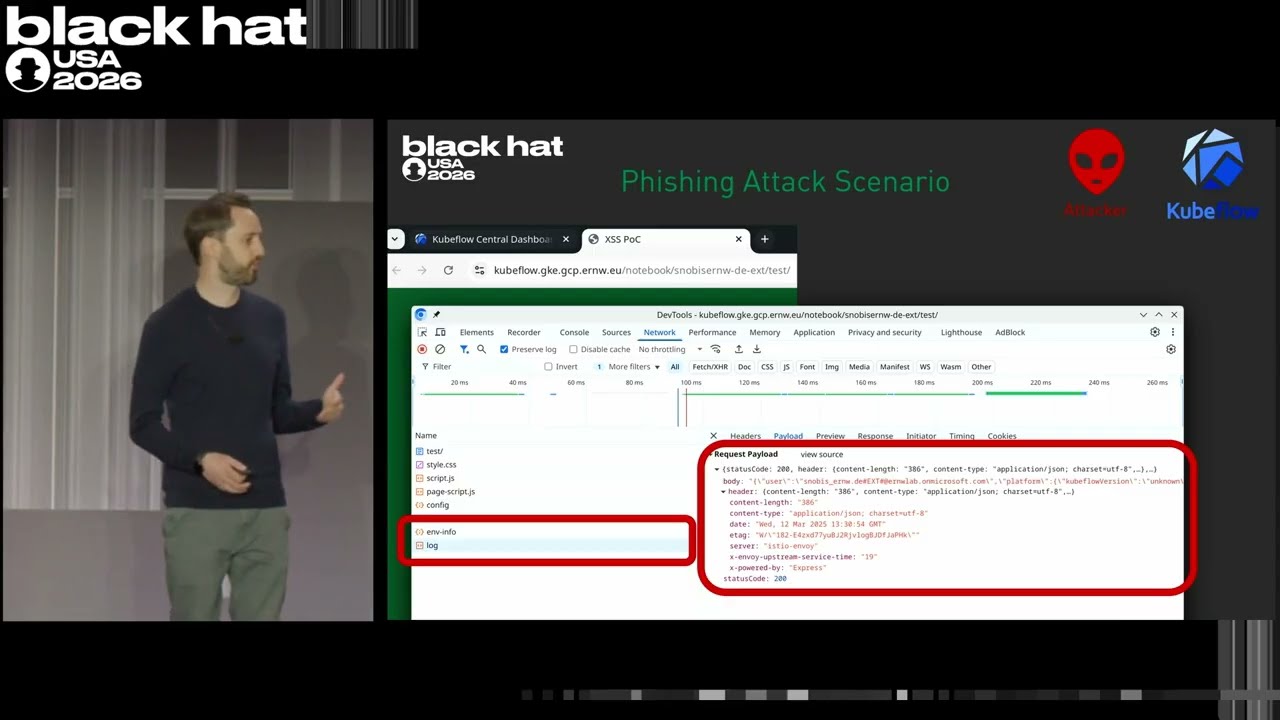
• In Kubeflow, tenants can create Istio Virtual Services that reference the global gateway, allowing them to intercept and log session cookies of other users for impersonation 8:19-9:54.
• By manipulating these Virtual Services, attackers can bypass network policies to access internal services like KServe, override user ID headers to impersonate service accounts, and extract cluster-admin tokens 11:14-14:46.
• Insecure cross-namespace references also exist in annotations, such as in Traefik, where tenants can reference service transports from other namespaces to bypass mutual TLS authentication 23:59-24:30.
• Data plane vulnerabilities in Istio allow tenants to create Virtual Services that act as a man-in-the-middle, intercepting inter-service traffic by specifying arbitrary hosts 26:43-27:13.
• A recommended mitigation methodology involves assessing tenant capabilities, identifying control plane and data plane interactions, and applying custom policies to restrict dangerous references 28:20-34:53.
These findings highlight that multi-tenancy risks often extend beyond the cluster to cloud infrastructure, necessitating rigorous assessment of application-level access controls.
Sources:
- 2:01-2:18 Introduction to the research question: whether industry best practices are sufficient for Kubernetes multi-tenancy.
- 8:19-9:54 Demonstration of cookie interception via cross-namespace Virtual Service references in Kubeflow.
- 11:14-14:46 Explanation of vertical privilege escalation to cluster admin via KServe and header manipulation.
- 23:59-24:30 Analysis of insecure cross-namespace references in Traefik annotations.
- 26:43-27:13 Description of data plane vulnerabilities in Istio service mesh allowing traffic interception.
- 28:20-34:53 Presentation of a three-step methodology for identifying and addressing multi-tenancy weaknesses.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cloud Security. Commonly maps to: Security Architecture and Engineering, Communication and Network Security. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone and welcome to our talk. Today we want to show you how we broke multi-tenancy over and over in Kubernetes and what we can learn from this. But before we start who we are, my name is Lorin and this is my colleague Sven Nothnagel. We both work as a security analyst at the company of ERNW, a security consulting company located in Heidelberg in Germany. And here in the background you can see the rest of our team, the people who we work with and they're here in the slides because we basically want to give them a big thank you for their support. And yeah, we would like to start our talk with a question. How many of you use Kubernetes and maybe your company does? Or your customers? And if the answer is yes as I see, perfect because you are our target audience. You are the people wh…