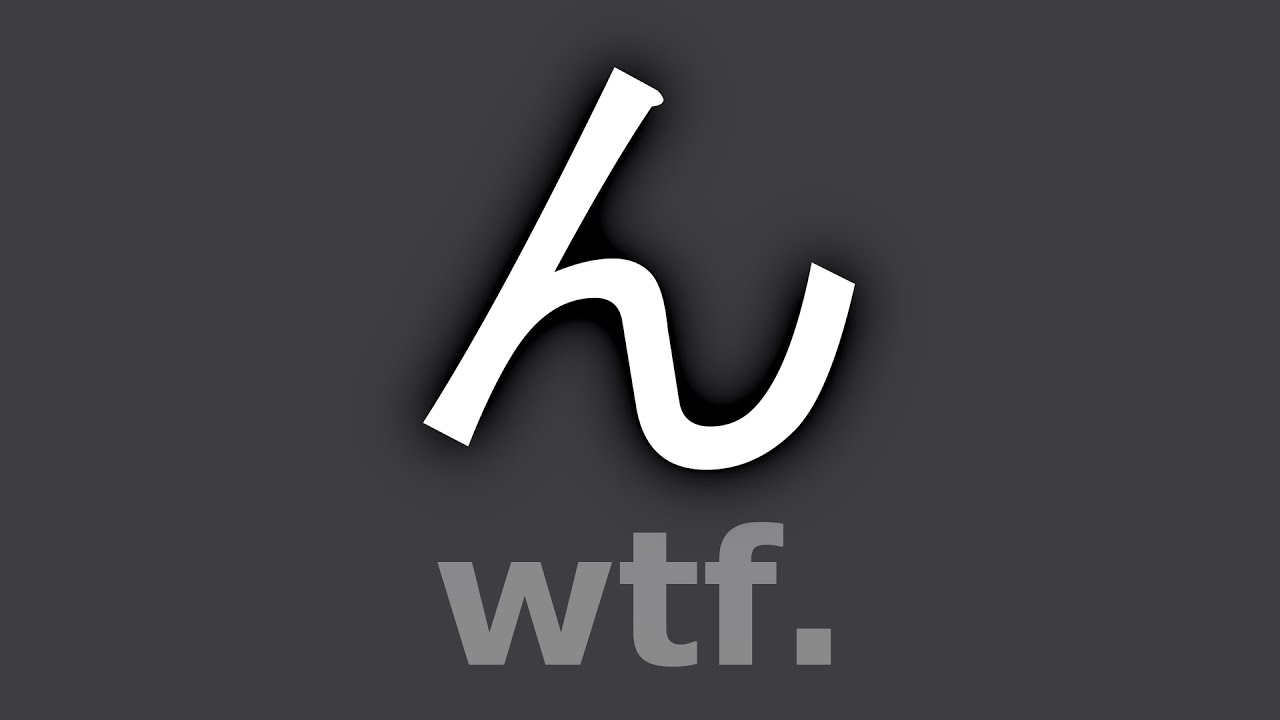
this symbol is LYING TO YOU
Source: YouTube · John Hammond · published Aug 20, 2025 · 16:45
A new Booking.com phishing campaign uses a Japanese hiragana character resembling a forward slash to create deceptive URLs that appear legitimate 0:07-0:17.
Key Takeaways:
• Attackers use the Japanese hiragana character (Unicode hex 3093) that visually resembles a forward slash in URLs, making malicious links appear legitimate 1:01-1:14
• The technique allows bad actors to create domains that begin with legitimate-looking elements like "account.booking.com" followed by the deceptive character 2:14-2:20
• These phishing campaigns typically distribute infostealer malware designed to capture passwords, credentials, and session tokens 3:21-3:33
• While browsers now block most Unicode characters in domains, this specific hiragana character still renders in address bars, making it particularly dangerous 15:15-15:19
Security awareness and careful URL inspection remain essential defenses against these homoglyph attacks that continue to evolve despite browser protections.
Sources:
- 0:07-0:17 Introduction to homoglyph phishing attack using Booking.com
- 1:01-1:14 Explanation of the Japanese hiragana character resembling a forward slash
- 2:14-2:20 How attackers structure deceptive URLs with lookalike domains
- 3:21-3:33 Information about malware distribution via these attacks
- 15:15-15:19 Demonstration of which Unicode characters still work in browsers
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Oh, it's back everybody. The old lookalike characters, the old social engineering and fishing trick, the homoglyph. Honestly, it really never left. Booking.com fishing campaign uses sneaky that squiggly character to trick you. I saw this hit the interwebs just a bit ago on Twitter or X, whatever you want to call it. Now, of course, a bleeping computer article out and about where thread actors are leveraging a Unicode character to make fishing links appear like legitimate links. Booking.com, specifically in this case, a new campaign distributing malware. Of course, the attack makes use of the Japanese hiragana character, I hope I'm getting that pronunciation right, which can on some systems appear as a forward slash. So like folders or directories or just the usual slashes that you see in y…