DEF CON 33 - LLM Identifies Info Stealer Vector & Extracts IoCs -Olivier Bilodeau, Estelle Ruellan
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 49:52
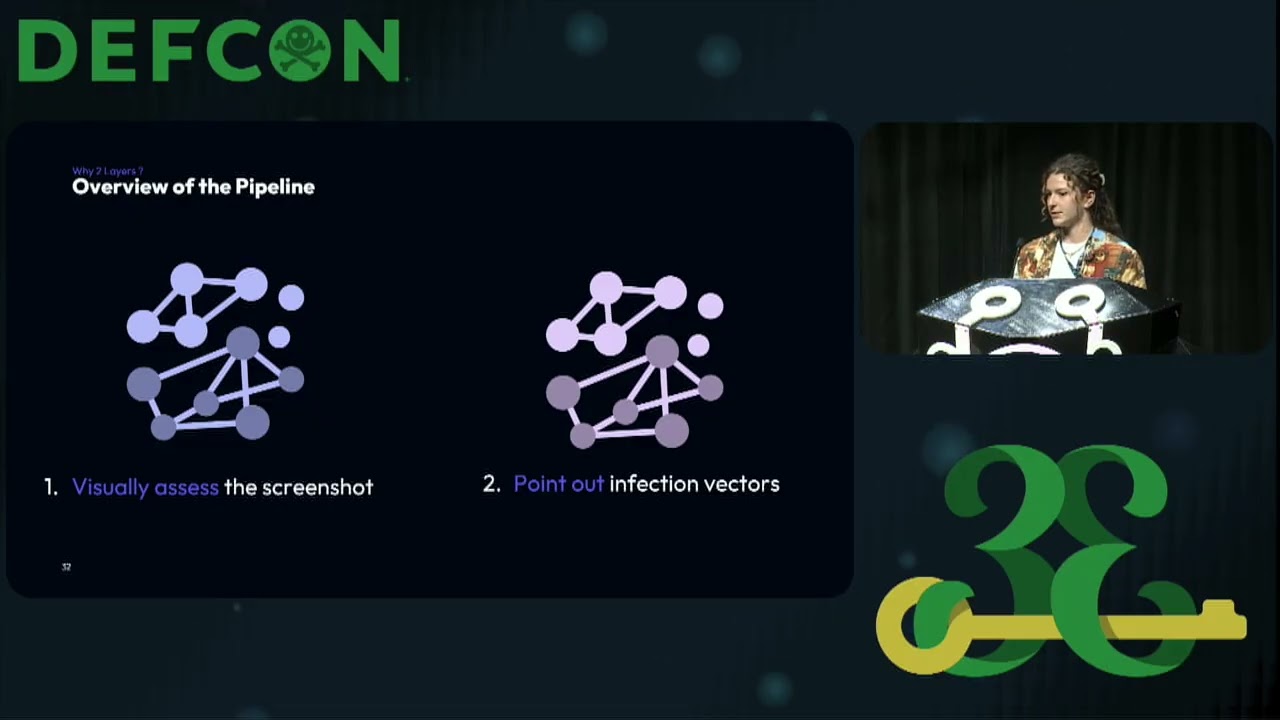
The presentation demonstrates how to use a two-layer LLM system to analyze screenshots from information stealer malware infections, enabling large-scale extraction of IoCs and tracking of cybercriminal campaigns 0:18.
Key Takeaways:
• Information stealer malware typically infects users through cracked software and gaming cheats, with criminals taking screenshots during infection that provide valuable forensic data 2:19
• The two-layer LLM approach uses one layer to describe screenshot content and another to identify infection vectors, which proved more effective than a single-layer system 5:48
• Common infection themes include cracked creative software like Midjourney and gaming cheats for popular games like Fortnite and Valorant 22:33
• Cybercriminals leverage distribution platforms like YouTube and Google Ads to reach victims, with YouTube videos often containing download links and instructions to disable antivirus 25:23
• The approach has limitations including reliance on screenshot quality and existence, with plans to expand analysis to other artifacts like process lists and browser history 40:16
The presentation highlights how breaking down analyst intuition into precise instructions allows LLMs to effectively analyze malware artifacts at scale, enhancing rather than replacing security researchers 39:37.
Sources:
- 0:18 Introduction to the topic of LLM identifying information stealers
- 2:19 Explanation of why criminals take screenshots during infections
- 5:48(https://www
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All right, we have the content is so packed that we're going to like stroll through it, but so here's a slide about bragging about ourselves. Let's get right into it. First, I I guess I should read our title. So, hacker dropping mid heist selfies, LLM identifies information stealer, infection vectors, and extract IoC's. This is a mouthful, but we'll get through it. big agenda and um first you need to understand and we'll go through together the agenda. So don't worry, don't you know don't feel bad. But first I need to set the record straight about uh uh information stealer malware. You need to understand to see what we're doing with this. So information stealer malware people uh usually infect themselves. They download uh cracked software is one of the big vector but so it goes through you…