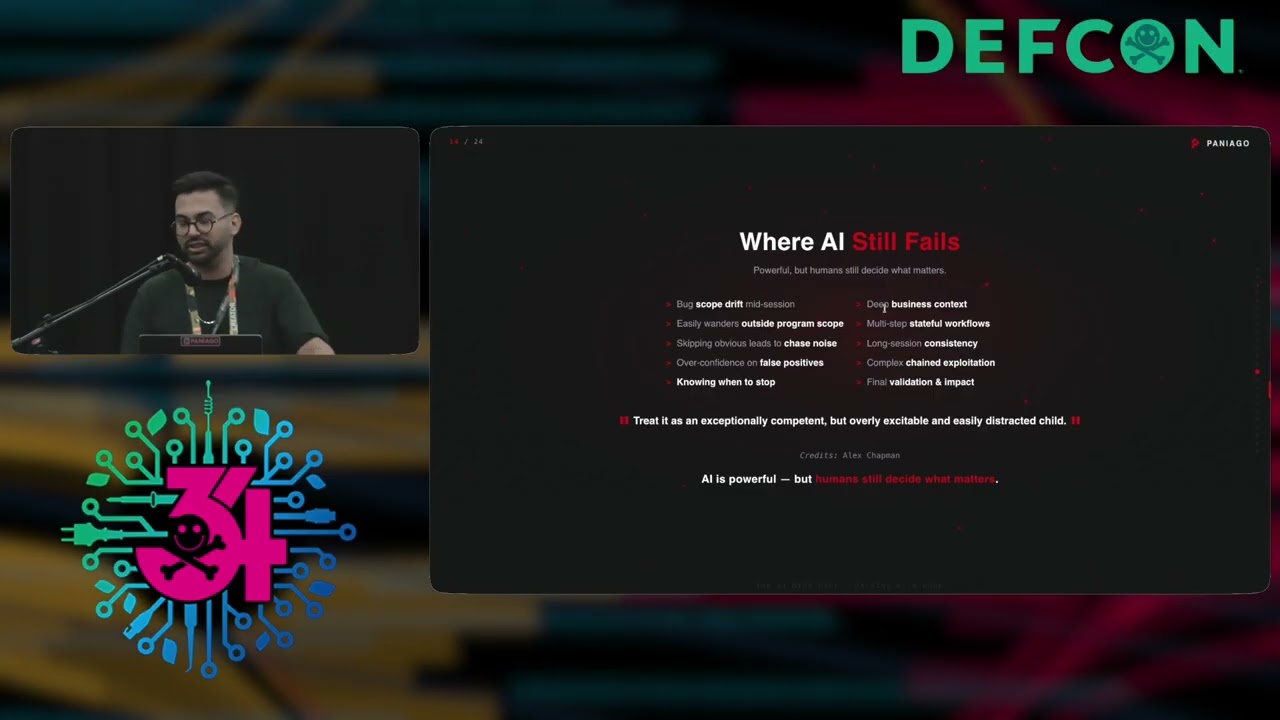
DEF CON 34 - BugBounty - AI Nightmare Hacking at 0 Hour - Pedro Paniago
Source: YouTube · DEFCONConference · published Nov 6, 2026 · 24:51
AI-assisted bug bounty has matured beyond low-hanging fruit: the speaker finished #1 in a live hacking event with 14 bugs and $25k in two weeks—without manual hunting 4:44.
Key Takeaways:
• Vanilla prompting fails; scaffolding (CLAUDE.md, scope, credentials, translated methodology) enabled auth bypasses, IDORs, business logic bugs, and account takeovers 3:39
• Standout criticals: gVisor sandbox escape unlocking 41 root capabilities, zero-click ATO via rogue ADFS certificates, and a GraphQL cross-tenant read/write bug 6:13
• AI still fails often—out of scope, weak business context, overstated impact: "exceptionally competent but overly excitable and easily distracted, like a child" 10:46
• Tips: sandbox it, prefer methodologies over workflows, recon is king, use multiple models, take notes, leverage /loop and /go for autonomous hunting 12:10
• New paradigm: AI does 80%, humans triage and validate; the real challenge is context, memory, methodology tuning, and cost control 16:12
• "Zero hour era": CVE weaponization fell from ~2.5 years to ~2.5 days; the AI reversed a TeamCity CVE in 5 minutes 18:39
The real threat isn't AI replacing hackers but everyone getting faster—developers and defenders need the same weapons 24:00.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
So thank you everybody for joining today. It's it's nice to see so many family felicas there. Um I wanted to thank Bugbat village for the opportunity so and the goons for helping me out. So everything started beginning of this year uh in January uh I was there and I think was a consensus about everybody in bug bing space say okay AI can only find lowhanging fruits it's just a hype and our job is safe but at the same time I saw like some open source tools using AI and then cloud code hype and expo outperforming all the bug bounty hunters on hack one I said what is going on there Right. So I said I start to become a little bit curious about AI. So then I said okay but to align a little bit everybody here maybe you guys are not familiar with like the whole workflow of a bug bounty hunter open…