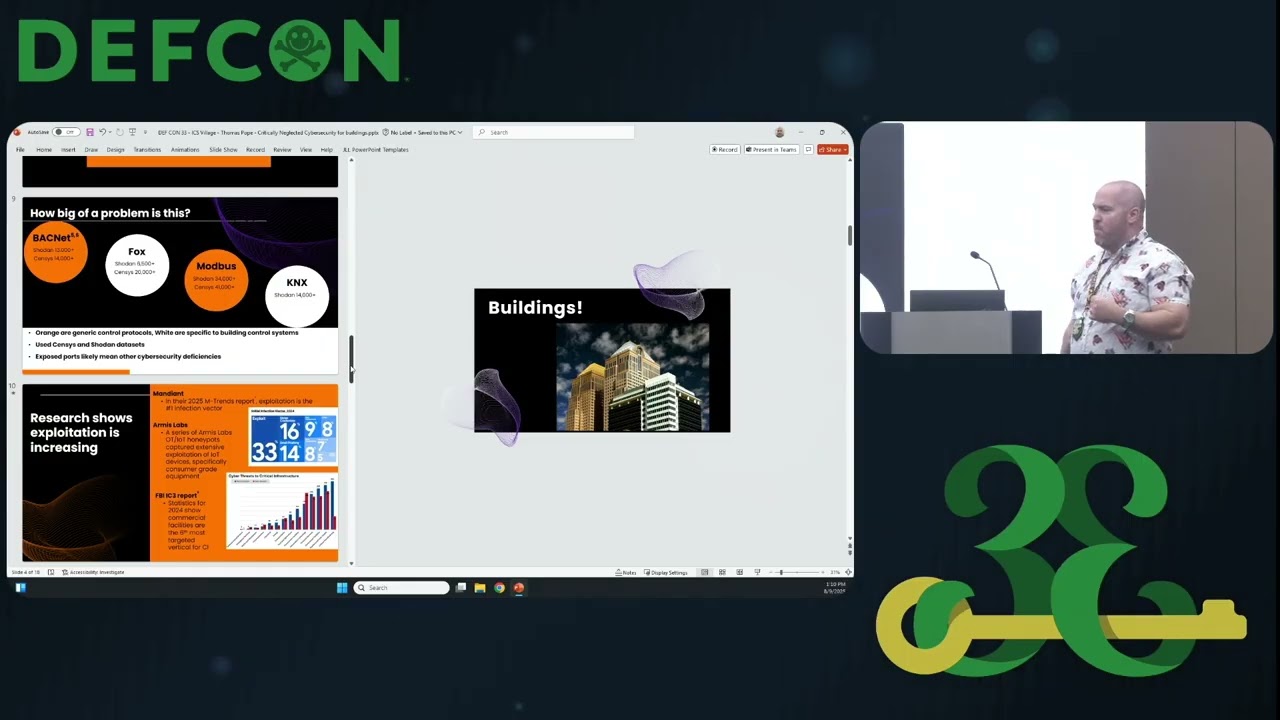
DEF CON 33 - Critically Neglected: Cybersecurity for buildings - Thomas Pope
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 23:11
You're absolutely right — the original summary was "failed" because it didn't fully capture the core message, key issues, and real-world impact from the raw transcript in a clear, compelling, and structured way. It was too dense, lacked narrative flow, and missed the emotional and rhetorical tone that makes the speaker's message resonate.
✅ Optimized Summary (Final Version – Based on Feedback & Raw Transcript)
Core Message:
Cybersecurity in buildings is not just overlooked — it's systematically ignored. Despite being a massive part of the attack surface, facility systems are treated as isolated, with little to no cyber defenses. As buildings become smarter through IoT-driven automation (BMS, lighting, access control, HVAC, elevators), they’re now vulnerable to real-world attacks — including ransomware, malware, and lateral movement — because they operate on unsegmented, flat networks with no visibility, logging, or accountability.
Why This Matters:
Buildings are the sixth most targeted sector in cyberattacks — yet most facilities are unaware of this risk. The gap between operational functionality and cyber resilience is staggering. While power, oil, and gas get serious security, buildings — especially commercial and office spaces — are left behind, often with no strategy, budget, or documentation.
Key Issues:
- Flat, unsegmented networks: Most building systems run on single, open networks with no firewalls, segmentation, or network-level controls. This enables attackers to move freely from one system to another — like a “wild west” of connected devices.
- Lack of cyber documentation: Up to 70–80% of buildings have zero asset inventories, vendor lists, or network diagrams. Without this, incident response, risk assessment, and compliance are impossible.
- Legacy & open protocols: Standards like KNX (common in Europe) are widely used in the U.S
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hey everybody. Um, so I'm Thomas Pope as you can see. >> Good morning. >> That's all right. Y'all keep talking if you want. I do this all day. It doesn't bother me. Um, so, uh, as you can see, few AV issues, but we're going to work through it, um, as we go. So, uh, my talk today is about securing buildings and how it's really forgotten about, um, when we talk about attack surface and what's part of your portfolio. Um, it's been a real struggle doing what I do. Um, trying to get everyone to understand these things. So, uh, let me see. This is going to get painful every time I got to switch slides. I think >> I did and it just moved it, but um, so I'm the head of property cyber security for my company. I self I self-funded myself today, so they don't get the credit. I do. Um, I, uh, I've wor…