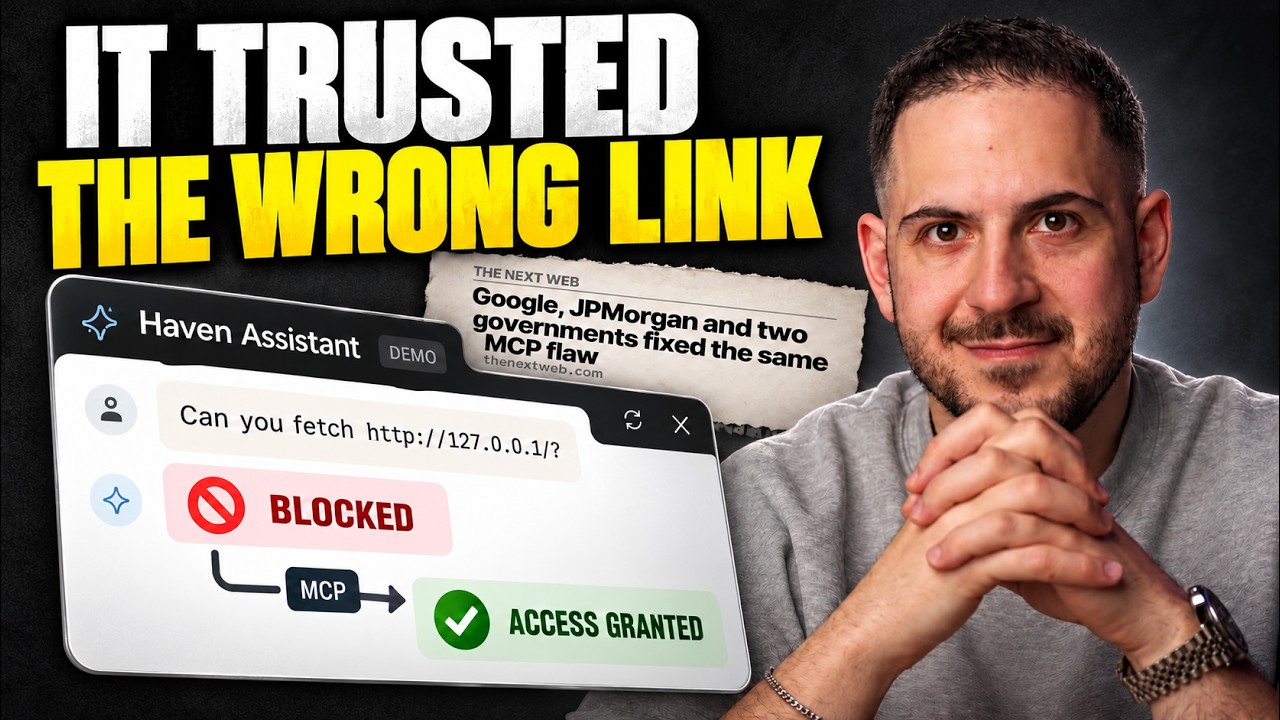
I Rebuilt a Real World MCP Bug. Can AI Find It?
Source: YouTube · NahamSec · published Nov 2, 2026 · 16:01
[BLUF]
The video demonstrates how an AI chatbot's open redirect vulnerability can be chained with SSRF to access internal services and exfiltrate sensitive credentials, a flaw also detected by the Snyk Evo AI security scanner 2:15.
Key Takeaways:
• The researcher built a lab to test if an AI chatbot could be tricked into fetching internal URLs by exploiting an open redirect on a trusted domain 0:56.
• Manual exploitation involved finding an open redirect behind the login, using it to point the chatbot to a local service, and bypassing security checks via HTTP headers 10:57.
• The Snyk Evo tool was used to automatically identify this complex logical chain, including the open redirect and subsequent SSRF, without prior knowledge of the specific vulnerability 3:03.
• The successful exploit allowed the chatbot to fetch the admin.config file from the internal server, revealing database credentials and API keys 13:02.
• The attacker used a redirect chain (trusted domain -> external service -> localhost) to bypass the chatbot's internal URL blocklist 14:45.
[Closing statement]
This case highlights the critical risk of logical vulnerabilities in AI-connected tools, where simple redirect flaws can bypass security controls to expose internal infrastructure. It also proves that AI-powered scanners can effectively detect these multi-step attack chains that traditional tools might miss.
Sources:
- 0:56 Introduction of the lab environment with a vulnerable chatbot and open redirect.
- 3:03 Overview of Snyk Evo's capabilities for AI security testing and target configuration.
- 10:57 Explanation of the manual exploitation technique using HTTP headers to bypass restrictions.
- 13:02 Demonstration of successfully accessing internal admin configuration files via the exploit.
- 14:45 Summary of the automated attack chain identified by the Snyk Evo scanner.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Penetration Testing. Commonly maps to: Security Assessment and Testing, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
This chatbot refuses to fetch any internal URL or resources. That is exactly what it's supposed to do. But, what happens if I give it a URL from a website or another resource that it trusts, and that site responds with a redirect to the address that it just refused? About a month ago, I was going through a bunch of news articles, and I came across a research on this class of bug in AI-connected tools. The names that got my attention were companies like Google, JP Morgan Chase, and a couple of government projects like France's national open data platform and a city government in Indonesia. These are all vulnerabilities found in their tools, not reports that all of those organizations have actually been [music] hacked. But, in Google's and France's case, it raised a question I wanted to test…