DEF CON 32 - Navigating the Turbulent Skies of Aviation Cyber Regulation - M. Weigand, S. Wagner
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 54:46
The video outlines a critical gap in civil aviation cybersecurity: commercial aircraft lack real-time antivirus or intrusion detection systems, despite increasing connectivity and reliance on software. The speaker advocates for mandating continuous monitoring of avionics in new aircraft designs, a change enabled by the recently passed FAA reauthorization act. Key takeaways include the importance of telemetry data for learning and adaptation, the need to break down industry data silos, and the potential for hackathons to drive innovation in aviation security. A major challenge is balancing rapid threat response with aviation safety standards that require long software certification cycles.
• Current aircraft lack onboard cybersecurity tools like antivirus or intrusion detection, despite growing software dependency 3:30.
• The FAA reauthorization act now requires cyber security and continuous monitoring in new aircraft designs—a shift from previous suggestions to a formal requirement 5:44.
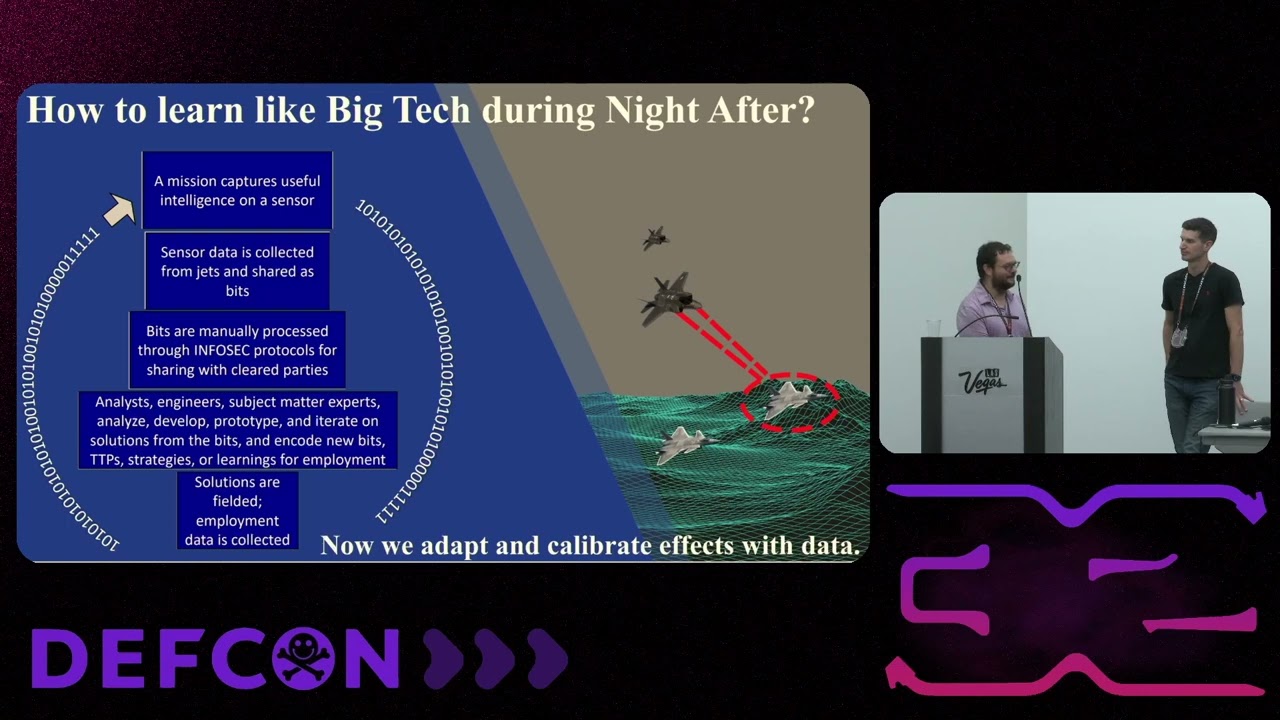
• Lessons from Air Force hackathons demonstrate how operational data can be used to build real-time monitoring systems and detect anomalies, offering a model for civil aviation 11:00.
• Pilots emphasize the need for crew alerts to detect malicious software or system failures, stressing that current training does not cover such threats 32:00.
Cybersecurity in aviation must evolve from reactive fixes to proactive, data-driven monitoring. While real-time alerts remain a challenge due to pilot workload, the long-term value of continuous data collection for predictive maintenance and threat detection is clear. The policy path forward requires inclusive, cross-sector collaboration to develop standards that balance safety, security, and operational efficiency.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
hey everybody thank you so much for coming uh welcome to Flying Blind where we're going to talk about uh Aviation policy we're going to share some lessons learned from uh uh from our experience in the Air Force and in uh in civil aviation everything from Capitol Hill to actually um hacking uh hacking some fighter jets today so thank you my name is Michael wagens and I'm joined today by hey I'm steuart Wagner just a little bit of background on ourselves um I am a a reformed army officer and recovering entrepreneur um I uh I I served in the Army as one of the first cyber officers and then I decided I wanted to start a company so that we could bring hardware and software solutions to uh to the market to help protect aircraft because they don't have antivirus and stuff on it um it seemed like …