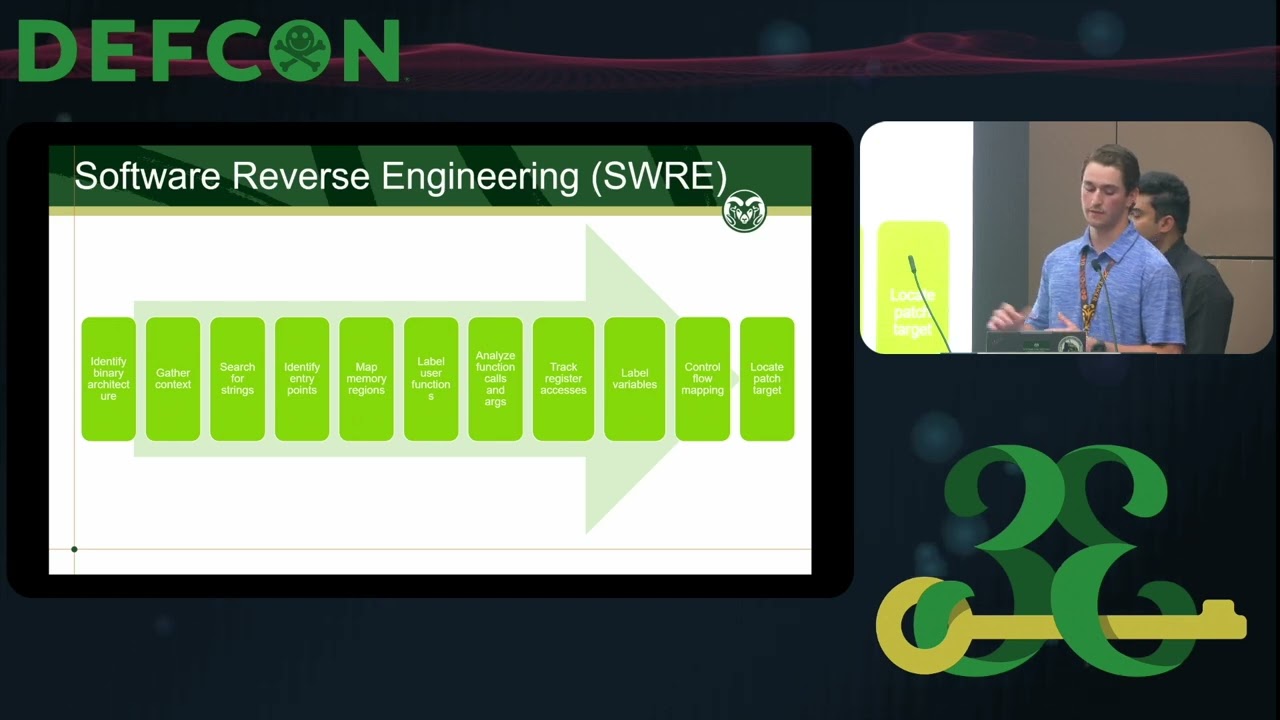
DEF CON 33 - Dead Reckoning: Hijacking Marine Autopilots - Carson Green & Rik Chatterjee
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 20:32
[BLUF: Researchers demonstrate a remote exploit of marine autopilots via CAN network address claim attacks, enabling full control over engine communication and highlighting critical vulnerabilities in maritime cyber-physical systems 5:00.]
Key Takeaways:
• A malicious firmware update can be uploaded to an autopilot over CAN without authentication, allowing remote code execution 9:31-9:57.
• The autopilot performs an address claim attack, claiming address 0 with a lower name priority value to displace legitimate devices like engine controllers 5:00-5:48.
• This results in the engine being removed from the network and unable to receive critical commands, demonstrating physical system takeover 19:33-19:58.
• The vulnerability is exploitable due to lack of authentication, firmware signing, and secure boot mechanisms in marine devices 14:05-14:21.
[The research underscores the need for stronger security practices in marine systems, including firmware signing, secure boot, and network authentication to prevent unauthorized control of critical infrastructure. A live demo shows the attack successfully removing an engine controller from the network via address claim manipulation.]
Sources:
- 5:00 Explanation of address claim attack and how it displaces legitimate devices
- 9:31-9:57 Firmware update process and reverse engineering steps
- 14:05-14:21 Recommended security practices for marine systems
- 19:33-19:58 Live demonstration of engine disconnection via address claim attack
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello and good afternoon everyone. Welcome to our presentation on hijacking marine autopilots. All righty. Let's start off with a video. This is a chart plotter that's updating an autopilot and what looks to be a very simple and routine update process. However, that's not the case here and that's what we are going to show you through this presentation. All righty. For those familiar with CAN data, uh what we have is the upgrade happening over the CAN network, sending all this data to the autopilot, which is a malicious firmware update. At this point, the autopilot then takes the update and reboots, and then it starts sending out what's called address claims. Uh this is something we'll talk about a little bit more later if you're not familiar with CAN. Uh but essentially we are taking contr…