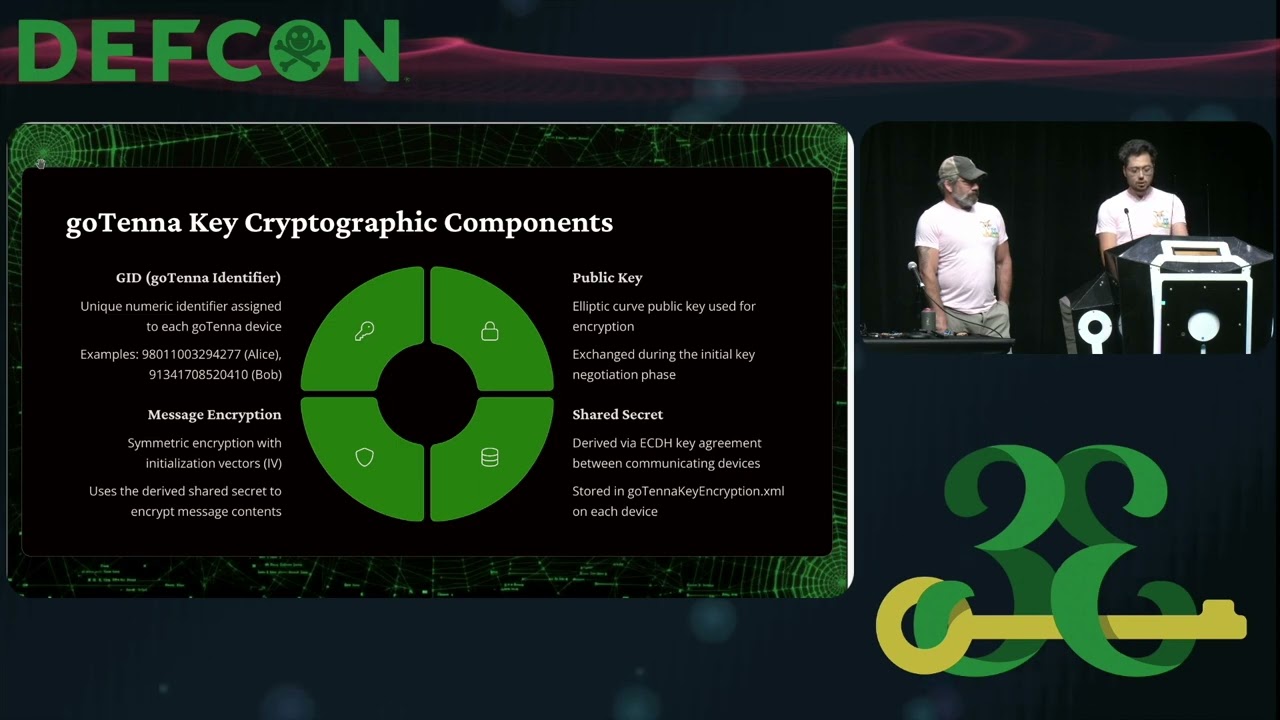
DEF CON 33 - One Key, Two Key, I Just Stole Your goTenna Key - Erwin 'Dollarhyde' Karincic, Woody
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 42:49
A critical vulnerability in Goenna Pro mesh radios allows unauthenticated remote key updates, enabling full man-in-the-middle attacks with undetectable tampering 3:37.
Key Takeaways:
• The vulnerability allows attackers to remotely update public keys without authentication, enabling full message interception and manipulation 3:37.
• Attackers can spoof identities, change GPS coordinates, and inject false messages—such as redirecting emergency locations—without users’ knowledge 18:42.
• The attack can be fully reversed, allowing attackers to restore communication and fool users into believing no compromise occurred 31:40.
• The vulnerability stems from a lack of key authentication in the device’s key exchange protocol, despite using ECDH encryption 9:01.
This vulnerability highlights the need for robust key authentication, real-time key verification, and operational protocols to detect and prevent unauthorized key updates—especially in mission-critical communications.
Sources:
- 3:37 Detailed explanation of unauthenticated key update and man-in-the-middle attack.
- 18:42 Demonstration of GPS coordinate spoofing in emergency scenarios.
- 31:40 Full attack reversal and undetectable communication takeover.
- 9:01 Technical breakdown of the elliptic curve key exchange implementation flaw.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Good afternoon everyone. Welcome to our presentation. So what we're going to discuss is a new critical vulnerability that that we have discovered in a in a essentially it's a new critical crypto vulnerability. Where we found this is in goenna pro device that is located right there. However, this process is very unique to what we discovered and it can be more generalized and and we advise other people as we as you go through this, if you're designing your own RF systems or something like that, look and see if you have vulnerabilities similar like these. Our presentation is titled one key, two key, I just stole your goener key. And Woody and I would also like to uh thank Clayton Smith for his assistance on this project. [Applause] So now that we go into this like first question is why does t…