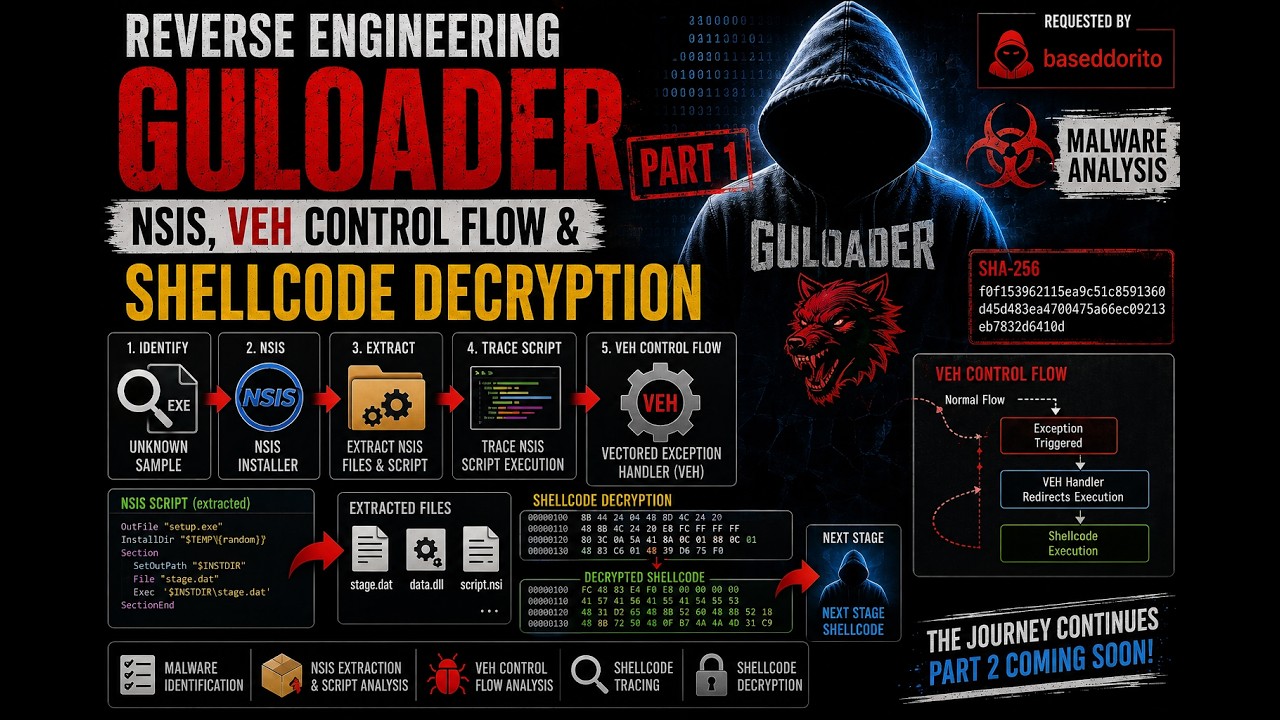
Reverse Engineering GuLoader | NSIS, VEH Control Flow & Shellcode Decryption Part 1
Source: YouTube · Malware Research Diary · published Aug 7, 2026 · 48:12
[BLUF] This video demonstrates the dynamic analysis of a sophisticated Inno Setup-packed malware dropper, highlighting techniques to bypass anti-debugging measures and extract shellcode using x64dbg. 0:05
Key Takeaways:
• The malware sample is an Inno Setup installer used as a sophisticated loader, detected by 52 AV engines as a generic GooLoader 2:27.
• Standard extraction tools like recent 7-Zip versions fail to reveal the internal script; analysts must use older versions (e.g., 15.05) to extract the NSIS script 6:30.
• The NSIS script configures the malware to drop files into hidden directories and establish persistence via the Windows Startup folder 9:09.
• Dynamic debugging with x64dbg is essential to trace the execution flow, as static analysis is hindered by complex control flow obfuscation 11:50.
• The malware employs anti-debugging techniques such as IsDebuggerPresent and int 3 instructions to detect and evade analysis environments 45:55.
• Analysts can dump the shellcode from memory by identifying the executable region in the memory map and saving it for further static analysis 26:14.
Closing Statement:
Effective reverse engineering of packed malware requires a combination of static script analysis and dynamic debugging to bypass obfuscation and extract the final payload for deeper investigation.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Welcome back to another um version of um malware hunting um research diary. Um today we thought I'm going to go over um briefly a first layer of a maleware sample that share by best Doritos um three days ago. So um so Doritos me um based based um Dorito mentioned that um analyzing this malware is a goo loader um malware um which is a very highly sophisticated um loader um using a lot of offisation um it is an incest um pack malware which is incis is a a setup or installation type of software solution that um able to packet a list of you know software for and you can just write script to deploy your software autom easily right so um this mailware using answers um answers to um deliver the the the malware um based on the information uh I found the the system DL um in plugin i…