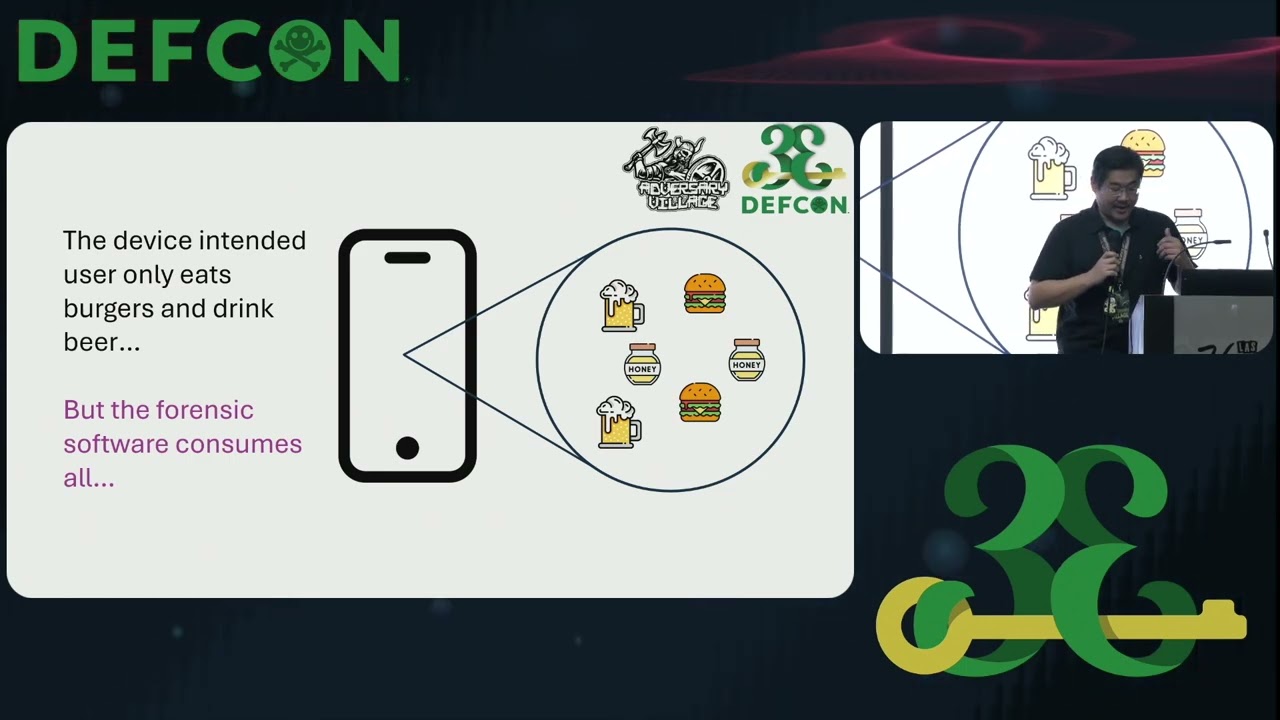
DEF CON 33 - Countering Forensics Software by Baiting Them - Weihan Goh, Joseph Lim & Isaac Soon
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 23:07
Researchers developed anti-forensic techniques using honey tokens that successfully compromise forensic tools like Celbrite, Axium, and Belosoft by triggering data encryption during extraction without detection.
Key Takeaways:
• Mobile forensics typically involves gaining device access, extracting data, and analyzing it, but this workflow is vulnerable to second-layer countermeasures
• Traditional anti-forensic approaches create obvious red flags that alert examiners
• Honey tokens are hidden bait files that trigger anti-forensic measures when accessed by forensic tools but remain invisible to regular users
• Using inotify, they demonstrated successful encryption of "crown jewel files" during extraction with major forensic tools
• For defenders, they recommend selective acquisition, understanding anti-forensic techniques, and thoroughly testing forensic tools
Their research shows long-standing forensic workflows may need rethinking to account for adversarial environments where gaining device access is just the beginning.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
All right. Uh, thank you for being here for this talk. How's stuff going so far for all of you? All right. Okay. Um, so the TLDDR of our talk today is, uh, we've developed some anti forensic techniques and, uh, it works against, uh, forensic tools like Celbrite, Axium, and uh, Belosoft. So my students here, they're going to show it to you a bit later about uh, you know, what we actually do and how we actually go about doing that. Right. So um first things first we're going to talk about the big picture why why we did this uh what's going on with the situation currently in terms of mobile forensics uh then we're going to talk a little bit about honey tokens which is the approach that we use uh honey tokens is like the trip wire right and once you deploy honey tokens you can basically do uh …