Hacking A Bank... (404 Bank - Part 6)
Source: YouTube · Tyler Ramsbey - Hack Smarter · published Nov 17, 2026 · 18:22
BLUF: The presenter transfers a password-protected configuration backup from a compromised domain controller to Kali Linux, cracks the password using a custom wordlist derived from the bank's website history, and retrieves disabled service account credentials to advance the Active Directory exploitation.
Key Takeaways:
• The presenter establishes an SMB share on Kali Linux using Impacket to receive config_backup.zip from the compromised web admin account on the domain controller 2:15.
• Standard unzipping fails due to AES encryption, prompting the use of zip2john to extract the password hash for cracking 4:42.
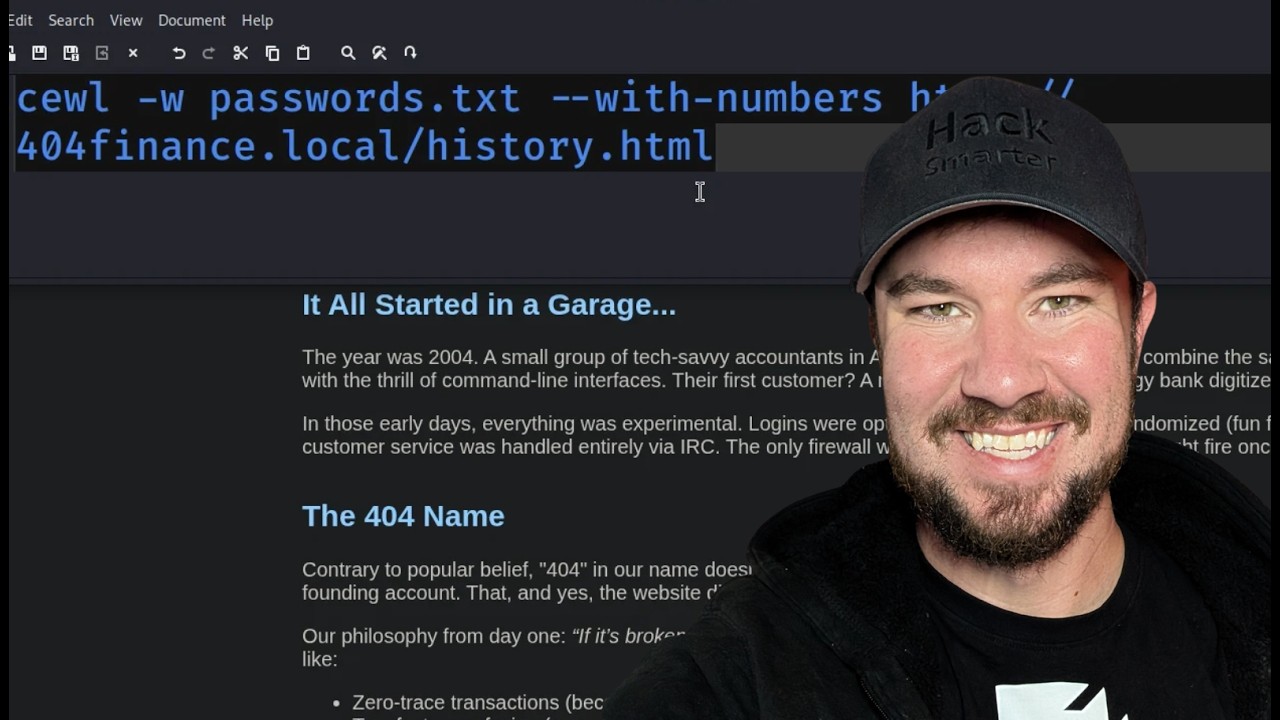
• John the Ripper fails with standard wordlists, leading to the creation of a custom dictionary using cupp based on the "Our History" page of the bank's internal site 8:41.
• The custom wordlist successfully reveals the password "Don't mess with Texas," which is then used with 7-Zip to extract config.dat 13:15.
• The extracted credentials are for the disabled SVC services account, which the presenter confirms via net use before assigning homework to re-enable it and exploit ADCS 16:23.
This process highlights the importance of context-aware password cracking and proper credential transfer techniques in penetration testing. The next phase involves leveraging these credentials to manipulate account states and exploit Active Directory Certificate Services.
Sources:
- 2:15 Setting up the SMB server with Impacket to transfer files.
- 4:42 Using zip2john to extract the hash from the encrypted archive.
- 8:41 Generating a custom wordlist using Cupp based on website content.
- 13:15 Successfully cracking the password and extracting the config file.
- 16:23 Verifying the disabled status of the SVC services account.
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Penetration Testing. Commonly maps to: Security Assessment and Testing, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
What is up everyone? Welcome back to another video. This video is part six of working through 404 Bank, which is an Active Directory lab from the Hack Smarter platform. We're going to pick up right where we left off in the previous video. Do want to let you know that you might see chat on the screen. As I record this, there are about 80 people in the live studio audience between YouTube, LinkedIn, and Twitch, but we are missing you. So, make sure you hit the subscribe button and hit the bell notification so you're notified the next time I am live. Hey, sorry on I'm not going to do a summary right now, Azana, only because we're starting the recording, but all of these will be posted as stand-alone videos on my YouTube channel. But, I'll give you a summary after we're done recording this par…