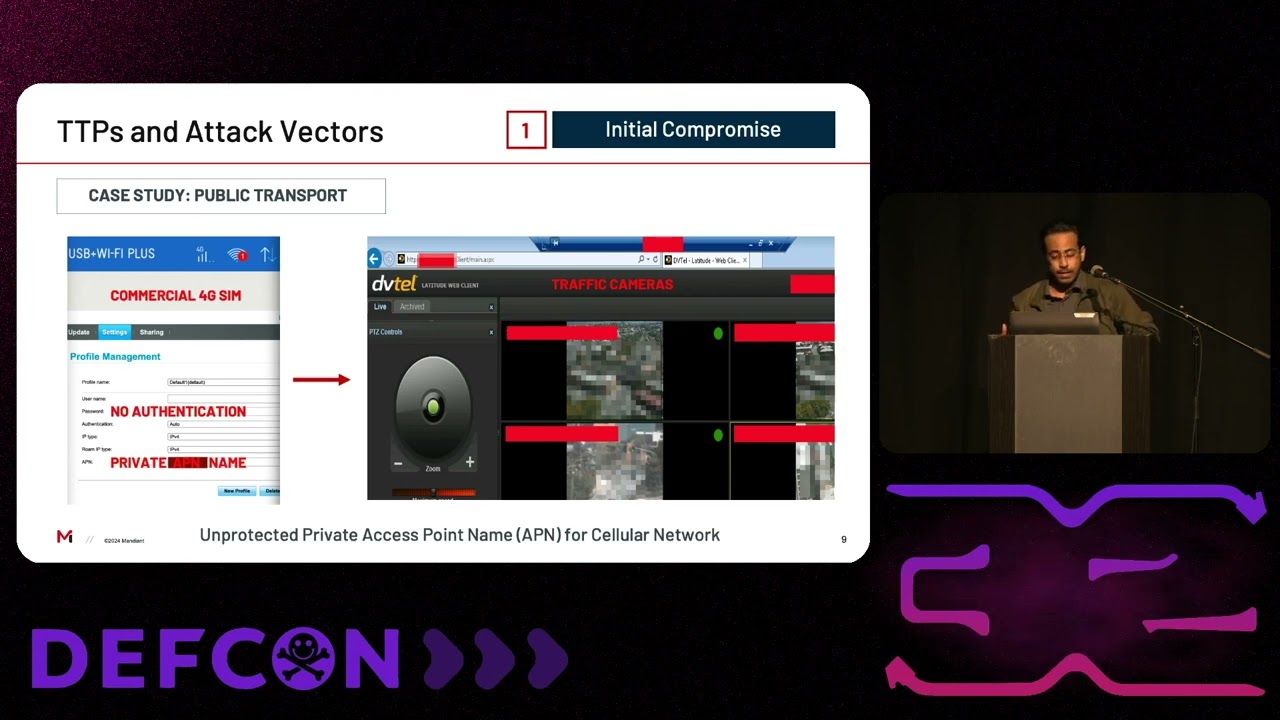
DEF CON 32 - War Games Red Team for OT Based on Real World Case Studies- Shishir Gupta
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 23:08
The presentation provides real-world examples of red team exercises against operational technology (OT) systems, demonstrating how attackers follow a multi-phase attack lifecycle rather than single-step compromises 3:26.
Key Takeaways:
• OT systems require specialized security approaches as they control critical physical processes across power, transportation, manufacturing and other infrastructure 1:37
• Initial compromise often occurs through insecure wireless networks, unauthenticated cellular networks, or enterprise network breaches 5:30
• Internal reconnaissance focuses on gathering network diagrams, documentation, and credentials from enterprise systems before targeting OT 9:53
• Network propagation commonly exploits segmentation flaws like shared infrastructure, domain trusts, or compromised credentials 13:32
• Mission execution ranges from simple HMI command abuse to sophisticated control logic manipulation, with process disruption being easier than manipulation 16:03
Defenders must understand the complete attack lifecycle and implement controls across all phases, not just at the OT level 22:26.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
um hi everyone uh it's really hard to see uh everyone with this slide uh so if if you cannot hear me just just shout out and I'll try to adjust the microphone can everybody hear me cool uh good afternoon everyone uh my name is shisher uh and I'm here to talk about red team and attack vectors uh for operation technology uh my objective here uh is to go beyond the hypothetical uh and I'm here to talk about red team and attack vectors uh a real world example for some of our red team exercises for critical infrastructure however uh before I start a quick disclaimer uh even though everything that I present here is based on real world case studies the content itself is highly reducted to remove any and all identifying information uh now we not here to talk about myself but uh it's still customar…