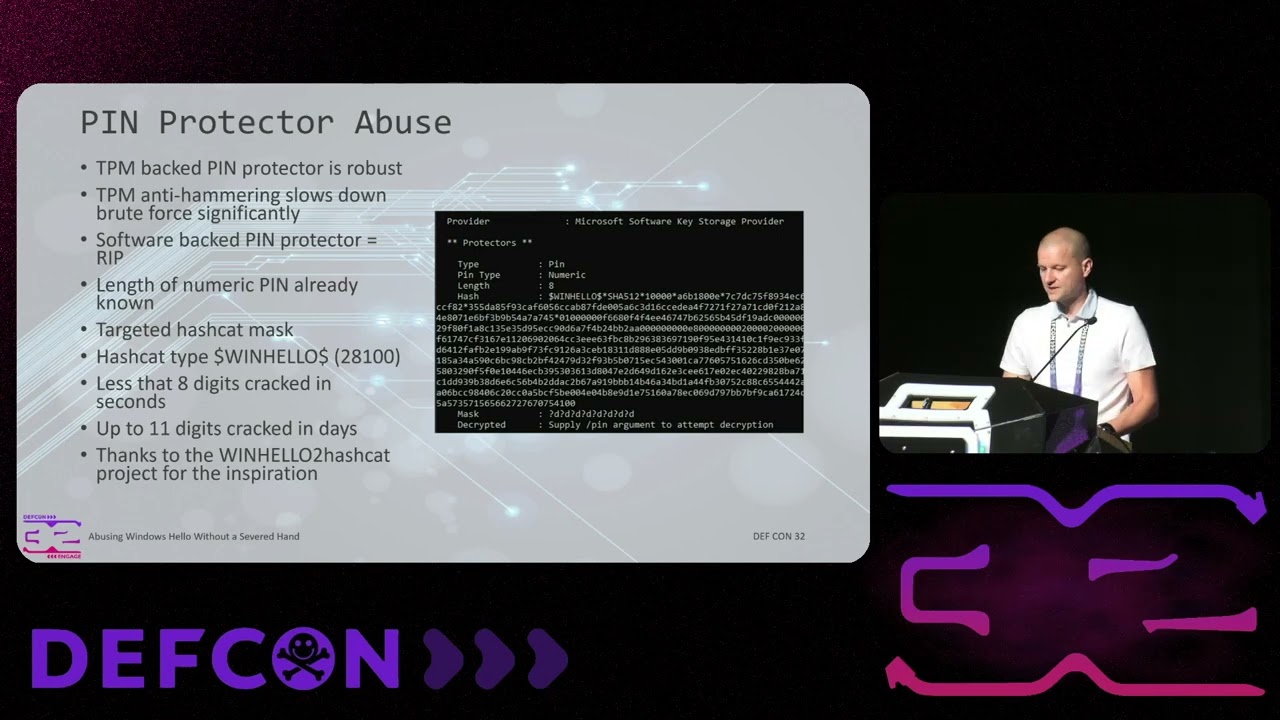
DEF CON 32 - Abusing Windows Hello Without a Severed Hand - Ceri Coburn, Dirk jan Mollema
Source: YouTube · DEFCONConference · published Nov 2, 2024 · 42:00
The researchers demonstrate critical vulnerabilities in Windows Hello's authentication system that allow attackers to bypass biometric protections and extract cryptographic keys 1:55.
Key Takeaways:
• Windows Hello uses a "Passport Key Storage Provider" that proxies to other key storage providers (software, TPM, or smart card) 3:50-4:05
• Biometric protectors are actually protected by system DP API keys, not biometrics, meaning system compromise allows bypassing biometrics entirely 11:09-11:24
• PIN protectors without TPM are extremely vulnerable - 8-digit PINs can be cracked within seconds using hashcat with known length information 10:30-10:44
The researchers released tools to demonstrate these vulnerabilities and recommended mitigations including Windows Hello Enhanced Sign-in Security (ESS), physical security keys, and proper endpoint monitoring 38:53-39:34.
Sources:
- 1:55 Introduction to Windows Hello and presentation structure
- 3:50-4:05 Explanation of key storage providers
- 11:09-11:24 Biometric protector vulnerability
- 10:30-10:44 PIN vulnerability without TPM
- 38:53-39:34 Mitigation recommendations
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
we're going to start by introducing Carrie hey get a hot one we're going to start by introducing Carrie and dirt abusing windows hillow with without a severed hand give a good hand for Carri and [Applause] dir good afternoon everyone uh so my name is Carrie uh I'm from Wales in the UN United Kingdom so my background is uh in software development uh I was in that world for around 18 years um within the DRM and security solution space and back in 2019 to this very def con week um I switched over to cyer Security and joined uh pentest Partners so I've been dedicated to Red teaming and offensive security for the last three years and have spoken at Defcon last year and various besides event as well um and I I am authored several tools on GitHub um mostly on the offensive security side uh but on…