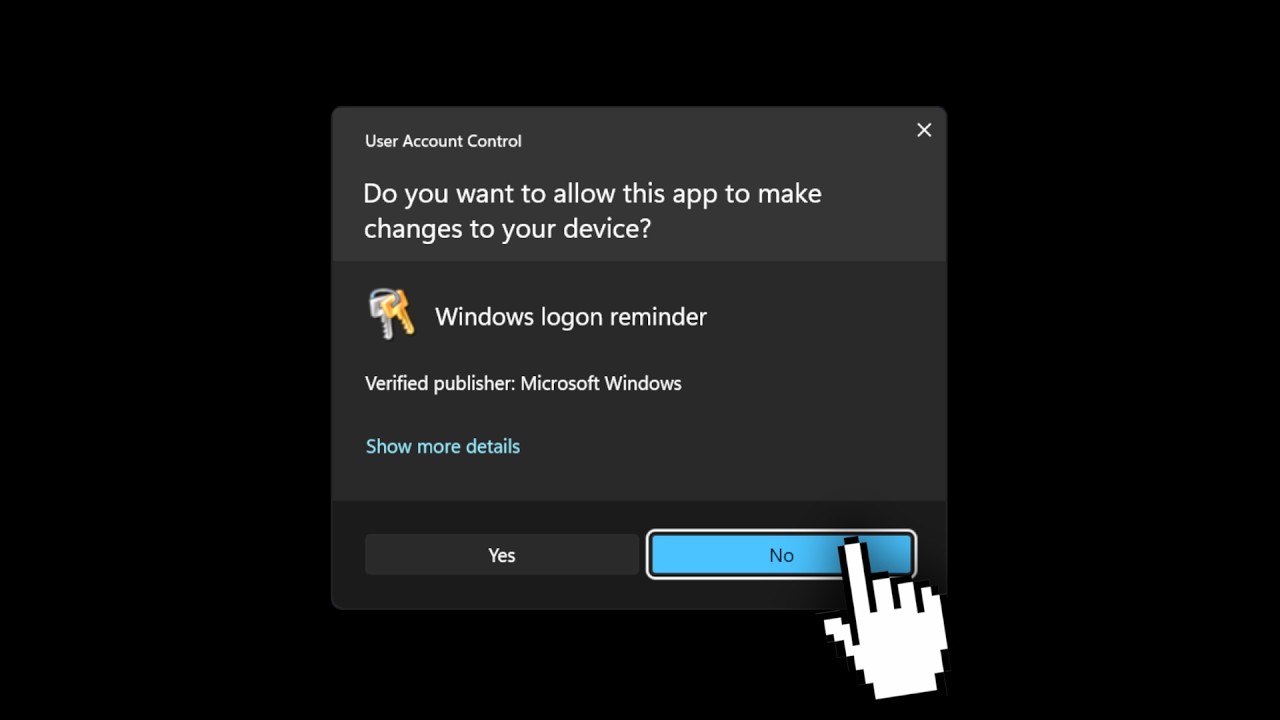
How Hackers Become Admin (they just ask)
Source: YouTube · John Hammond · published Oct 31, 2025 · 25:03
Here's the optimized summary based on the feedback and raw transcript:
Summary: The Nightshade C2 malware employs a "UAC prompt bombing" technique that relentlessly bombards users with administrator privilege requests until they grant access, effectively forcing privilege escalation 1:14-1:49. This attack exploits user frustration and system paralysis to achieve execution with elevated rights.
Key Takeaways:
• Loop Trap: The technique traps users in an endless UAC prompt loop, rendering their computer unusable until admin privileges are approved 2:44-2:53
• Exit Code Mechanism: Malware checks PowerShell exit codes ($?); a non-zero result (user denial) triggers the prompt loop to repeat 2:15-2:24
• PowerShell Implementation: The technique was recreated in PowerShell using a single-line command leveraging try/catch blocks and error handling to force persistent UAC prompts 3:23-3:30, 7:15-8:05
• Social Engineering: Attackers disguise prompts using legitimate Windows binaries (e.g., pcalua.exe, wlrmdr.exe) to appear trustworthy and evade suspicion 19:19-19:36
• Sandbox Evasion: The technique doubles as sandbox evasion—when antivirus services are disabled in analysis environments, the malware gets stuck in an infinite loop, thwarting dynamic analysis 23:02-23:37
UAC prompt bombing coerces users into granting admin privileges through psychological and technical pressure, enabling malware execution while simultaneously evading security analysis 15:09-16:03.
Sources:
- [0:00-0:19]
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
A new botn net emerges from the shadows. Nightshade C2. Now, this is an article and write up from Eentire shared just last month in September. And I'll leave a link, of course, to this in the video description if you're interested. This is a threat report from some of the hacker activity and tradecraft that they have been seeing. And I'm not going to go through this entire article, but I will pick out kind of some of the interesting parts and pieces that I want to highlight and play with. Looks like the initial infection started with ClickFix, of course, and they're also seeing some backdoored or Trojanized versions of other software like Advanced IP Scanner, ExpressVPN, Hypers SecureVPN, CE Cleaner, and a lot of other stuff. But when they get to the actual malware, the payload here, it's …