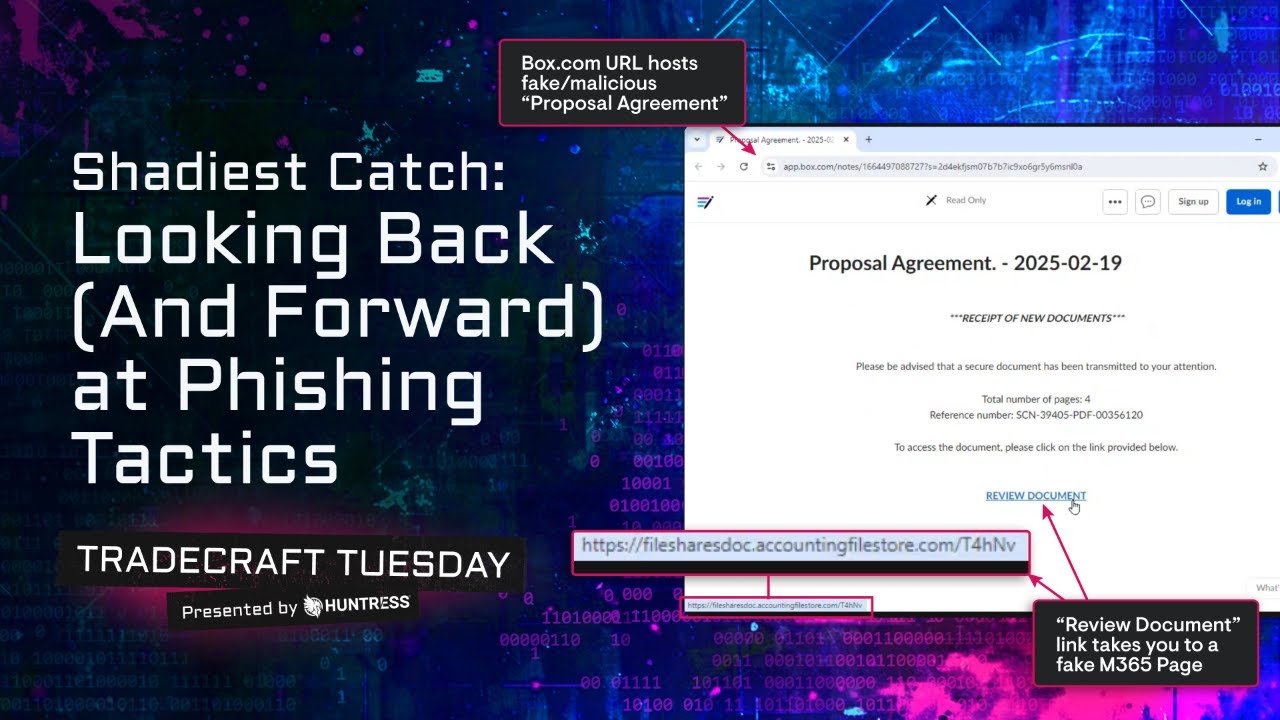
Tradecraft Tuesday | Shadiest Catch: Looking Back (And Forward) at Phishing Tactics
Source: YouTube · Huntress · published Nov 19, 2025 · 59:50
This webinar analyzes evolving phishing tactics, emphasizing the rise of platform abuse, sender spoofing, and AI-driven content to bypass traditional security controls.
Key Takeaways:
• Hosts engage the audience to share experiences with phishing templates, highlighting the prevalence of opportunistic attacks tied to current events 0:16.
• Google’s lawsuit against the "Smishing Triad" underscores the scale of SMS phishing scams, which have affected over 1 million victims globally 0:35.
• Attackers increasingly abuse legitimate platforms (e.g., DocuSign, DoorDash) to send emails from trusted domains, rendering sender inspection less effective 15:20.
• Voicemail lures and shipping notifications are common vectors, often using SVG attachments or image-based links to evade email security gateways 20:45.
• "Living off the land" techniques involve using trusted sites like Figma or Dropbox to host malicious landing pages, masking the final destination via redirects 35:10.
• Defense requires verifying unexpected alerts directly through official platforms rather than clicking links, even if the sender appears legitimate 45:30.
The session concludes that while AI improves phishing quality, layered verification and user skepticism remain critical defenses against sophisticated social engineering.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
of uh people from DC, Florida. >> Yeah, thank you. Thank you Lindsay for being here and thanks for having me. Uh thanks everyone for joining. Uh see I saw some UK in there as well. So good evening to you. Uh while we're kicking things off and before Lindsay continues, want you to throw into chat if you've sent fishing simulations, if you sent simulated fishing, what is your favorite kind of template or scenario you've sent out? And and you can say I've sent out this or that. If you haven't, what is the trickiest scenario you have received? Uh, so we're talking emails right now. I know smishing is a hot topic. We'll get to that in a minute. But, uh, email-wise, what is the trickiest email you've received? If you've not sent one out, feel free to to put both if you have. And, uh, I think it'…