DEF CON 32 - Nano Enigma Uncovering the Secrets in eFuse Memories - Michal Grygarek, Martin Petr
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 38:03
The video demonstrates how euse-based memory in ESP32 chips can be physically extracted and read using affordable, accessible tools, revealing secure boot keys and exposing flaws in traditional physical protection methods like layering. This proves that such security measures are easily bypassed with basic equipment.
Key Takeaways:
• Euse-based memory stores data permanently and can be physically read via microscopy after decapsulation 12:13.
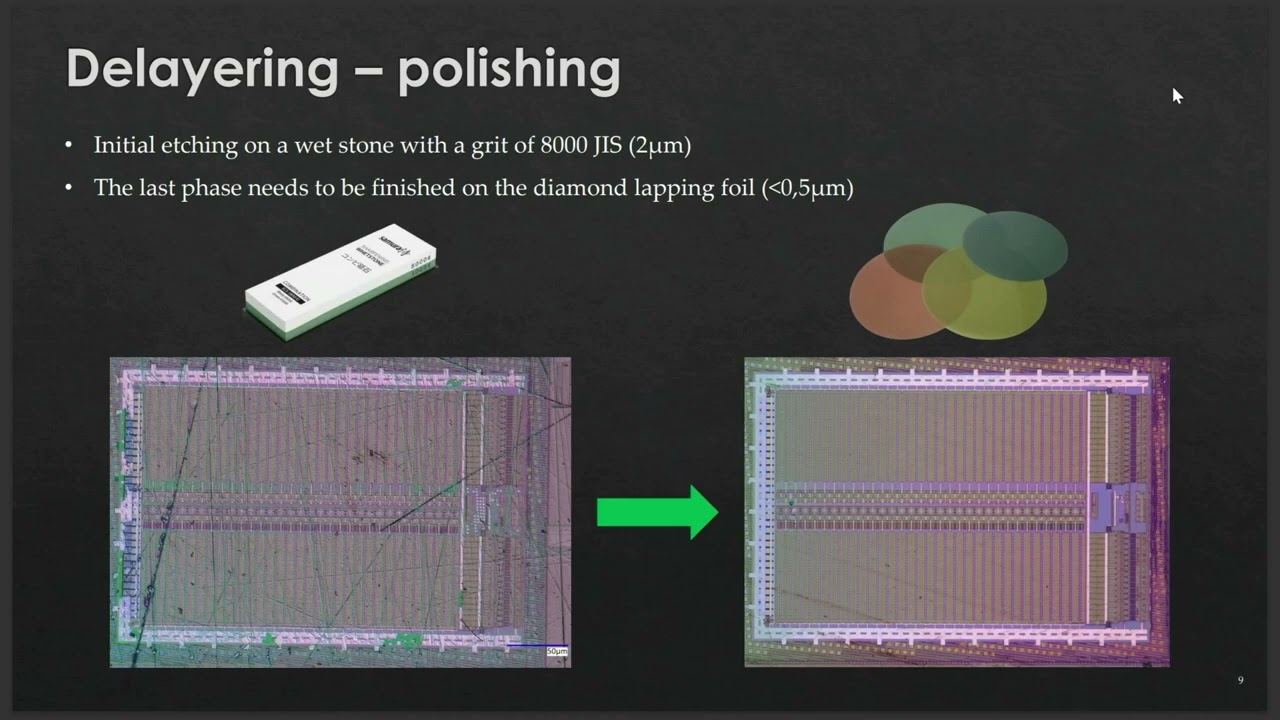
• Chips can be decapsulated using chemical methods or simple tools like red stone and diamond lapping, making attacks feasible at home 17:00.
• Scanning electron microscopy (SEM) enables high-resolution imaging to detect burned (1) and unburned (0) euses, with data extracted manually or via machine learning 14:00.
• A machine learning model achieves 99% detection accuracy by analyzing fused patterns in high-res images, automating the extraction of 64x64 binary arrays 27:00.
• The extracted flash encryption keys allow decryption of firmware, revealing hidden data like "hello Las Vegas" 34:00.
Euse-based memory is inherently insecure due to physical accessibility, and traditional protections like layering are ineffective against determined attackers with basic tools.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
hello I'd like to welcome you on our talk Nano Enigma uncovering the secrets within ifus memories uh first of all allow me brief introduction uh my name is Martin and I'm here together with my colleague mikal we also have a third partner in crime named hyan however he couldn't come here with us so we just have pre-recorded message from him uh we all work in the embedded system security testing team that's based in Prague Czech Republic which is under Accenture umbrella and we all have different fields of focus so for me that's reverse engineering so I'm usually that person that wants that firmware image un encrypted so making me shut up was partial motivation of this talk uh I'm pretty sure other guys will tell you briefly about themselves when their time comes so I'm just going to jump St…