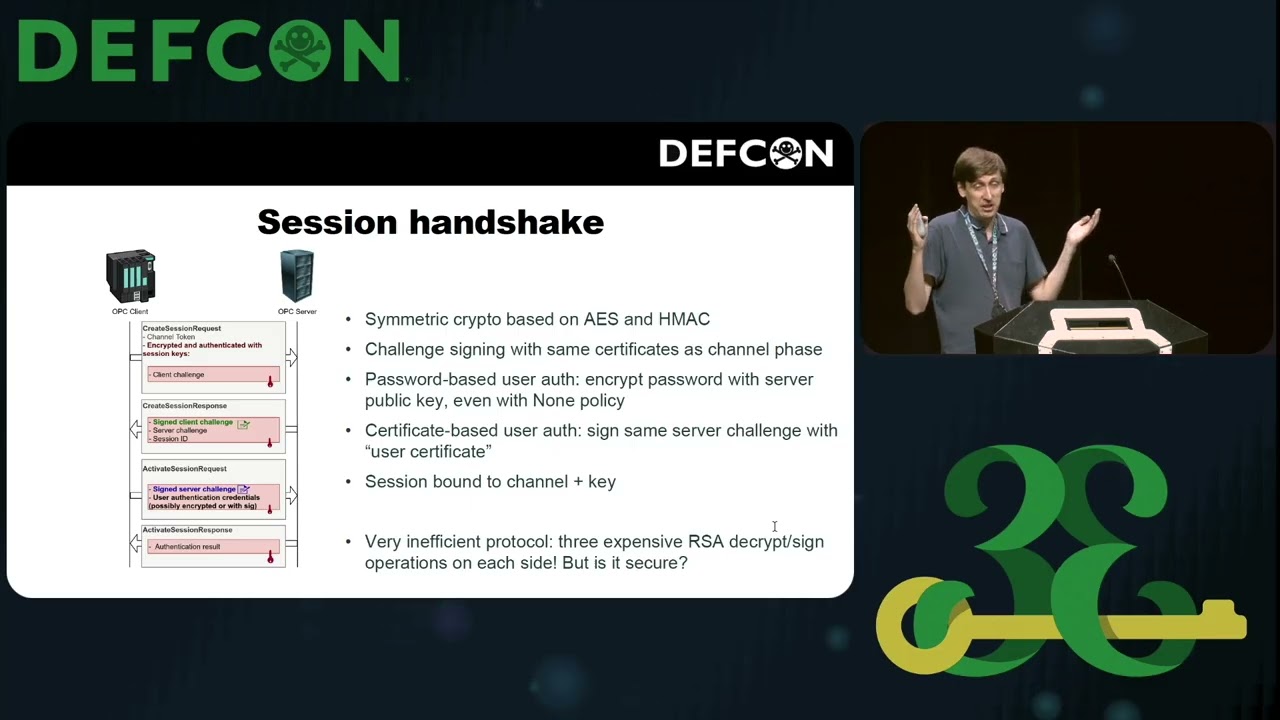
DEF CON 33 - No VPN Needed? Cryptographic Attacks Against the OPC UA Protocol - Tom Tervoort
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 36:17
Tom Fords discovered critical cryptographic vulnerabilities in OPC UA, an industrial automation protocol designed for secure cross-trust-boundary communication without VPNs.
Key Takeaways:
- Signing Oracle Attack (HTTPS Variant): A flaw in the HTTPS implementation allows for authentication bypass. Because the session layer signatures lack directional metadata, attackers can relay a challenge signed by one server to another. The HTTPS variant is specifically vulnerable because it skips the initial secure channel handshake, moving directly to the exploitable session layer.
- Bleichenbacher's Attack (PKCS#1 v1.5): The standard TCP variant is vulnerable due to its support for the deprecated PKCS#1 v1.5 padding scheme. By exploiting a timing oracle—where correctly padded messages take the server approximately 0.1 seconds longer to process—attackers can decrypt RSA messages and forge signatures. This "million message attack" can be executed in as little as 15 minutes.
- Prevalence: Testing revealed that 5 of 7 implementations were vulnerable, with 4 susceptible to attack in their default configurations.
- Disclosure and Remediation: The OPC Foundation coordinated the disclosure, resulting in CVEs and patches across multiple vendors. Fixes vary but include disabling the HTTPS variant, removing legacy ciphers, and mitigating timing oracles.
- Conclusion: The research demonstrates the difficulty of custom cryptographic protocol design. It emphasizes that established protocols like TLS should replace custom implementations and that deprecated encryption schemes like PKCS#1 v1.5 must be strictly disabled.
Source: Full Video
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Well, uh, welcome to my talk, uh, no VPN needed, cryptographic attacks against the OPCUA protocol. Uh, my name is Tom Fords. Uh, I work as a pentester, uh, general security consultant for Bureau of Fitas Cyber Security. Uh, and I'm personally based in the Netherlands. Um, when it comes to research projects, my specialization is kind of lies at the edge between uh, offensive crypto research and pentesting. basically trying to achieve uh useful uh well pent testing results poning things uh through practically exploitable cryptobox. Um I got a lot of publicity after I happened to find a flaw in an obscure protocol used for active directory that which led to the zero loon vulnerability and now I get to spend a lot of time on research projects such as this. So during this talk I'll first give a…