DEF CON 33 - Post Quantum Panic: When Will the Cracking Begin, & Can We Detect it? - K Karagiannis
Source: YouTube · DEFCONConference · published Oct 10, 2025 · 39:30
Revised Summary: The Quantum Encryption Crisis - Timeline Accelerated
The Threat: Quantum computing advances have created an imminent encryption crisis, collapsing what was once considered a "10-20 year" threat into a near-term reality. Current asymmetric encryption (RSA, ECC) – the foundation of digital security – is critically vulnerable to quantum attacks using Shor's algorithm, while symmetric encryption faces weakening through Grover's algorithm. This represents the first predictable "zero day" vulnerability in computing history.
Key Vulnerabilities & Timeline Acceleration:
- Technical Breakthroughs: Recent algorithmic optimizations have drastically reduced qubit requirements:
- RSA 2048-bit: From billions (2012) → 6,000 logical qubits (2019) → ~1,400 logical qubits (2023)
- Bitcoin/Blockchain: Attackable with as few as 1,754 logical qubits
- Hardware Projections: Ion Q projects reaching 800 logical qubits by 2027 and 2,000+ by 2028 – enabling encryption cracking within 5 years. IBM forecasts 2,000 logical qubits by 2033.
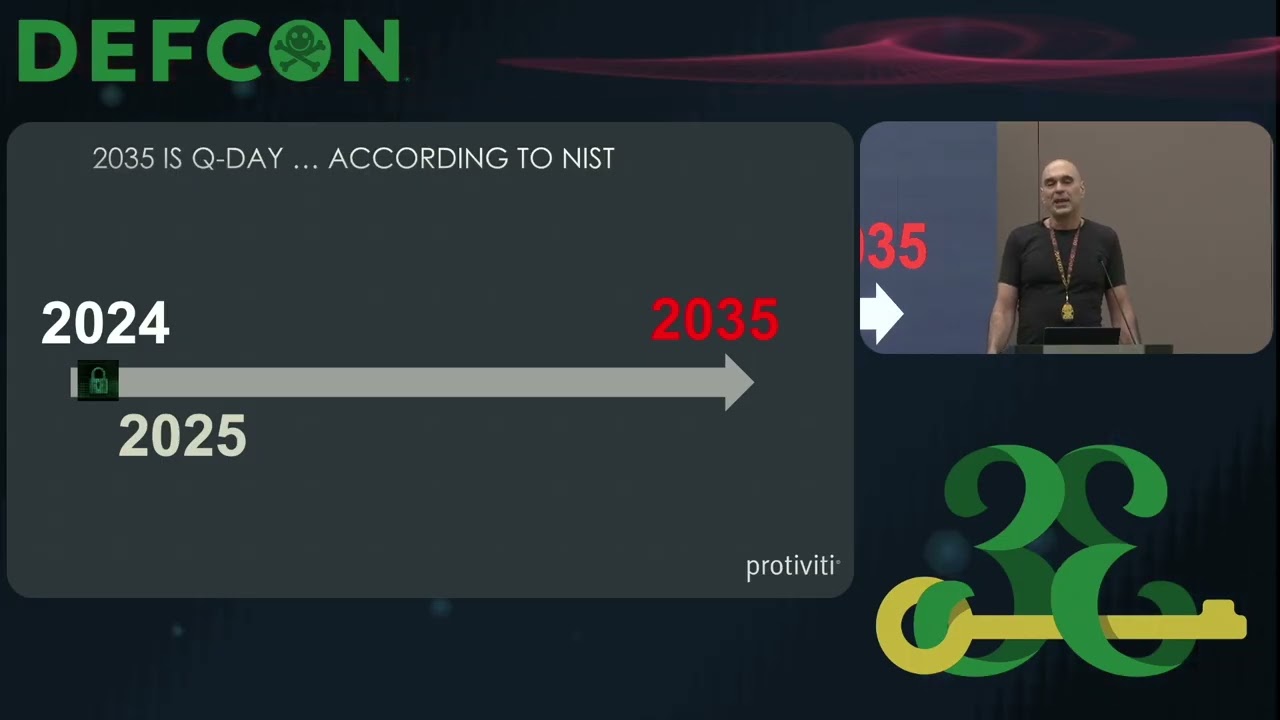
- NIST Timeline Conflict: NIST mandates migration to post-quantum cryptography (PQC) by 2035, creating a dangerous 5-year overlap (2028-2035) where critical systems will be defenseless.
Consequences of Inaction:
- Data Harvesting: Encrypted data intercepted today could be decrypted retroactively ("harvest now, decrypt later")
- Catastrophic Systemic Failures:
- Blockchain collapse (e.g., Bitcoin value plummeting to zero if private keys are reversed)
- Banking/financial infrastructure compromise
- Digital identity and signature systems rendered obsolete
- Attack Detection Challenges: While Shor's/Grover's algorithms are theoretically detectable, cloud providers (AWS/Ion Q) prohibit monitoring due to privacy policies. Primary attackers: nation-states and organized crime.
Urgent Solutions:
- Immediate Migration: Organizations must start PQC
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
So, postquantum panic. Ah, okay. Yeah, things are worse than they seem, I promise. Um, so we're going to be talking about uh Yeah. Uh, yeah, it's it's a fun story. I I've been in this in this business a very long time. Uh, I started in physics and I spent a lot of years doing pen testing, too. Weird, right? I did both. And, um, I was sort of waiting for quantum computing to catch up with me. And, uh, it did. It did. Uh we're we're finally approaching this this uh terrible day that we were all dreading. So it's it's time to get cracking here. And I hope to give you an idea of what the threat is, what we could do about it, and why I feel we don't have very long even though we used to think. I mean, when you used to ask people how long we had, it was always 10 to 20 years or, you know, some s…