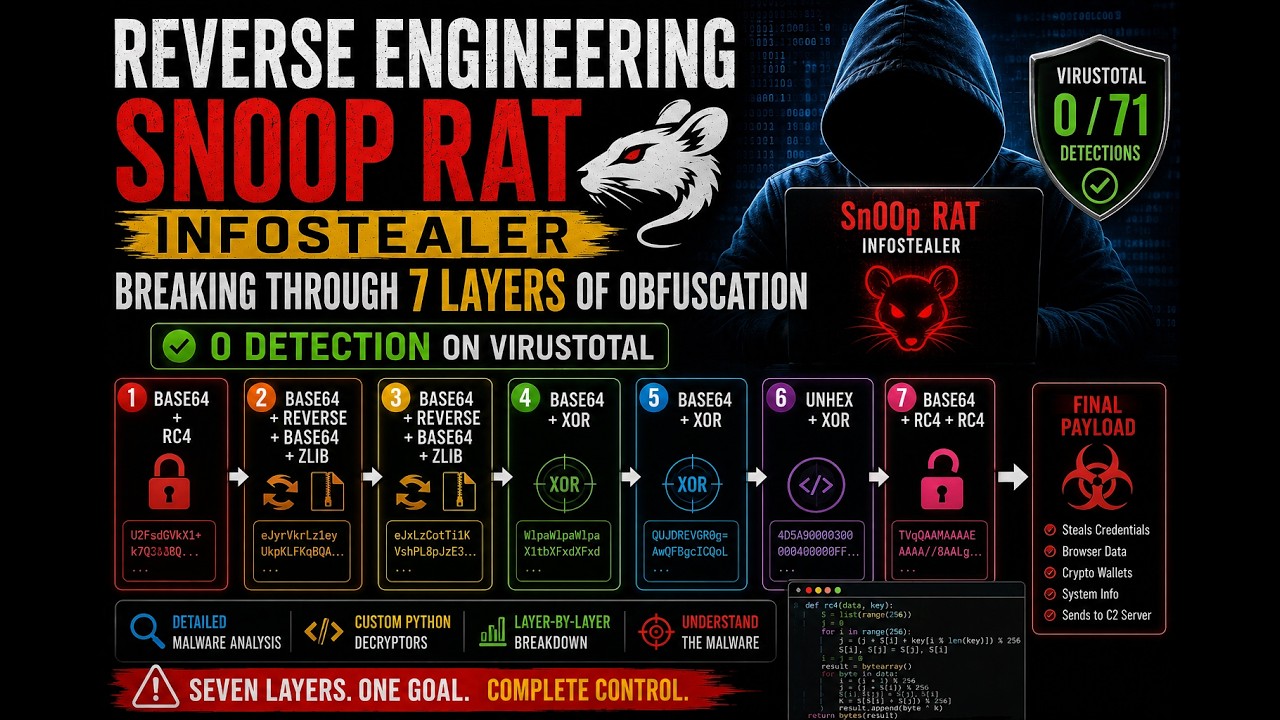
Reverse Engineering Sn00p RAT | Breaking Through 7 Layers of Obfuscation (0 Detection)
Source: YouTube · Malware Research Diary · published Jul 7, 2026 · 23:58
The video analyzes a newly submitted Python script, rank.py, which was misclassified as VBA by antivirus software but exhibits suspicious external connections and API calls 0:45.
Key Takeaways:
• The script rank.py was recently submitted and detected as undetected, though misclassified as VBA instead of Python 0:37.
• Analysis reveals external connections from the IP address associated with the malware 0:58.
• The malware performs API calls to snapcraft.io, a package management system for Linux, suggesting potential Linux targeting or environment detection 1:11.
• Memory inspection shows the presence of Telegram, IP addresses, and GitHub references, indicating potential command-and-control or data exfiltration capabilities 1:40.
This analysis highlights the importance of inspecting memory artifacts and external connections even when file type classification is ambiguous.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Malware Analysis. Commonly maps to: Security Operations, Security Architecture and Engineering. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Hello everyone. Welcome back to another session in huntings for malares. So today um we going to take a quick look at this um offication temp built rank.py. So let's take a look um obs. So I'm just going to show on vice total to see what it is. So seem to be undetected. Um summary zero 62 um misclassified as VBA instead of Python um and it's fairly new submitted today. So um from so there seem to be external um connection from for this IP address and let's see the behavior behaviors um so API calling um snap snap craft um io I don't know what this this. So let's see what this is. Just quick Google is a uni um okay snap un um it's a package management for Linux. So why is it so is this a Linux um application maybe? So in the memory is contain telegrams um IP GitHub JSON Python um Roblox Wik…