[SIG-Auth] Bi-Weekly Meeting for 2025-06-04
Source: YouTube · Kubernetes · published Jul 5, 2025 · 1:01:57
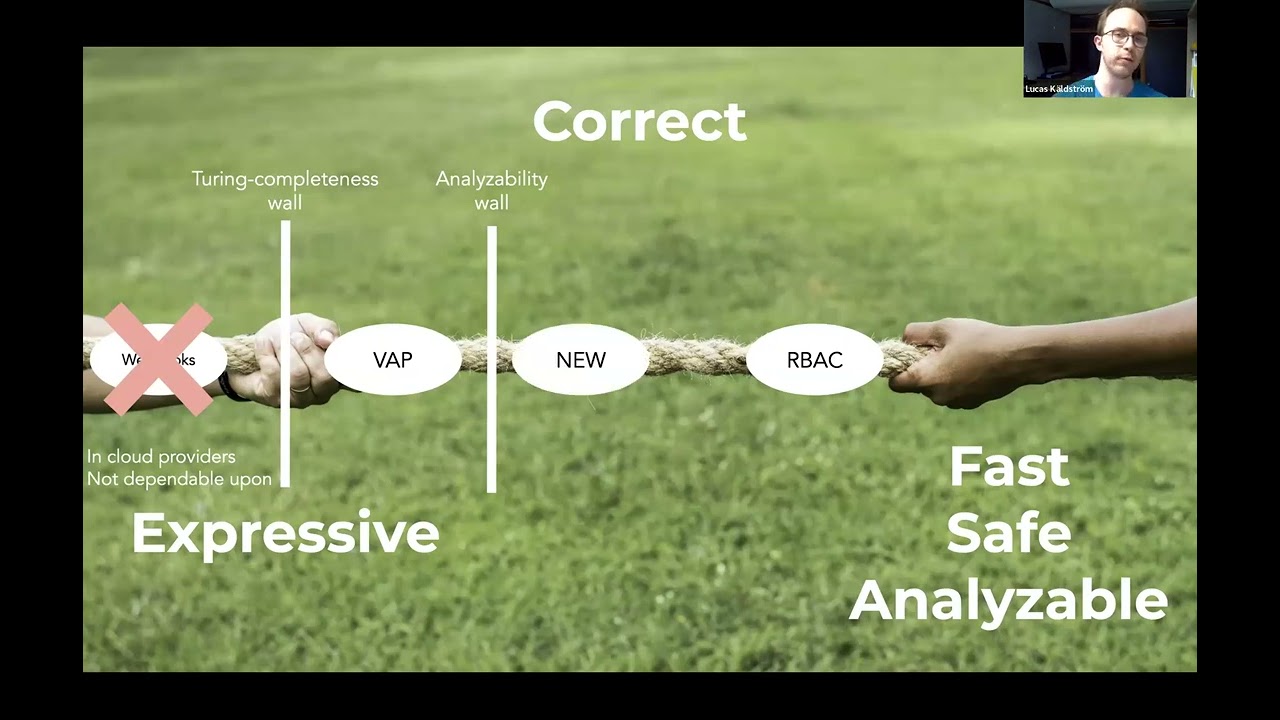
[The goal is to introduce a unified, analyzable conditional authorization system that improves security, simplifies policy writing, and enables fine-grained control over both read and write operations in Kubernetes clusters, using a subset of Cell/CRD expressions with SMT-based analyzability to prevent privilege escalation.]
• Unified authorization with label and field selectors for both read and write operations 17:18
• Conditional authorization enables partial evaluation and residual policy checks, allowing for safer, more consistent decisions at admission and authorization stages 22:00
• The proposed solution leverages Cedar’s analyzable SMT encoding to detect privilege escalation risks and ensure policy consistency without requiring full loops or complex expressions 28:45
• A key design choice is restricting expressions to avoid loops and quantifiers, ensuring analyzability while maintaining practical expressiveness for common use cases 30:00
This approach enables a consistent, user-friendly authorization experience across reads and writes, with built-in safety checks and backward compatibility, while leveraging existing tools like Cedar and proposing a forward-compatible implementation in the Kubernetes ecosystem.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 1 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Um hey everyone uh welcome to the SIGO community meeting. Today is June 4th 2025. This for this call is recorded will be published to YouTube. It follows the CNCF code of conduct. Uh so we have two items for discussion and then we have one demo. So maybe we can start with the demo. I think Lucas. Yes, thanks. Uh yeah, and it's a demo and kind of also a discussion item I guess um of you know what if we should make go forward with a cap uh for this um in this form for the conditional authorization feature. Um let's see if I Yeah, I think you need to approve the share screen requests for Okay, cool. Seems I have it nowhere. Can you see my screen? Yep. The Okay, cool. So, well, some time back u well this is about conditional authorization and let's see how we could use some of that. Uh the bac…