DEF CON 32 - V2GEvil: Ghost in the Wires - Pavel Khunt & Thomas Sermpinis aka Cr0wTom
Source: YouTube · DEFCONConference · published Oct 16, 2024 · 24:18
This presentation explores cybersecurity vulnerabilities in electric vehicle (EV) charging systems and introduces a security assessment tool called V2G evil 1:20.
Key Takeaways:
• EV technology creates new attack surfaces through charging systems 3:01
• Modern vehicles have charging ports connecting to previously isolated systems 3:35
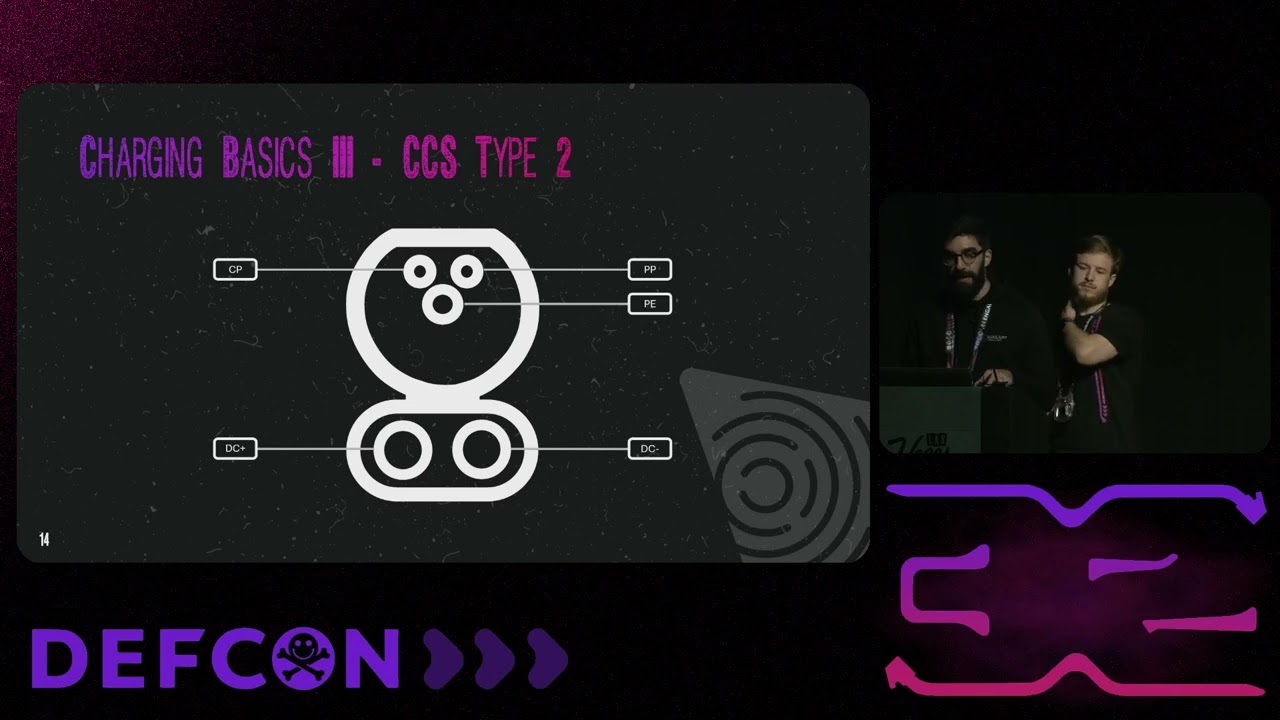
• CCS connectors include communication pins for data exchange 6:31
• ISO 15118 defines the V2G protocol with complex message exchanges 12:51
• V2G evil tool includes protocol analysis, sniffing, enumeration, and fuzzing modules 18:01
• The fuzzer module sends malformed data to exploit EV vulnerabilities 21:40
The presenters highlight the need for security research in this emerging field and plan to release their tool publicly after DEFCON 32 24:12.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
hello hello everyone first of all thank you for joining us today and our topic is v2g Will G in the wirs uh where will we talk about the v2g evil and the cyber security issues that come with it first of all let me introduce us I am pav Kon cyber security researcher and I'm C currently working at auxilium pentes lab with Tom yeah hello from myself too I'm Thomas RIS I'm the technical director of auxilium pendas slabs and yeah like let's let's start our main goal today uh is to analyze the state of cyber security in the automotive industry and get an in-depth look on the EV architecture and this undeniably emerging attack Vector we want to explore and understand the communication protocols used in EV charging today and introduce you to our security tool v2g evil uh that we built with Pavel d…