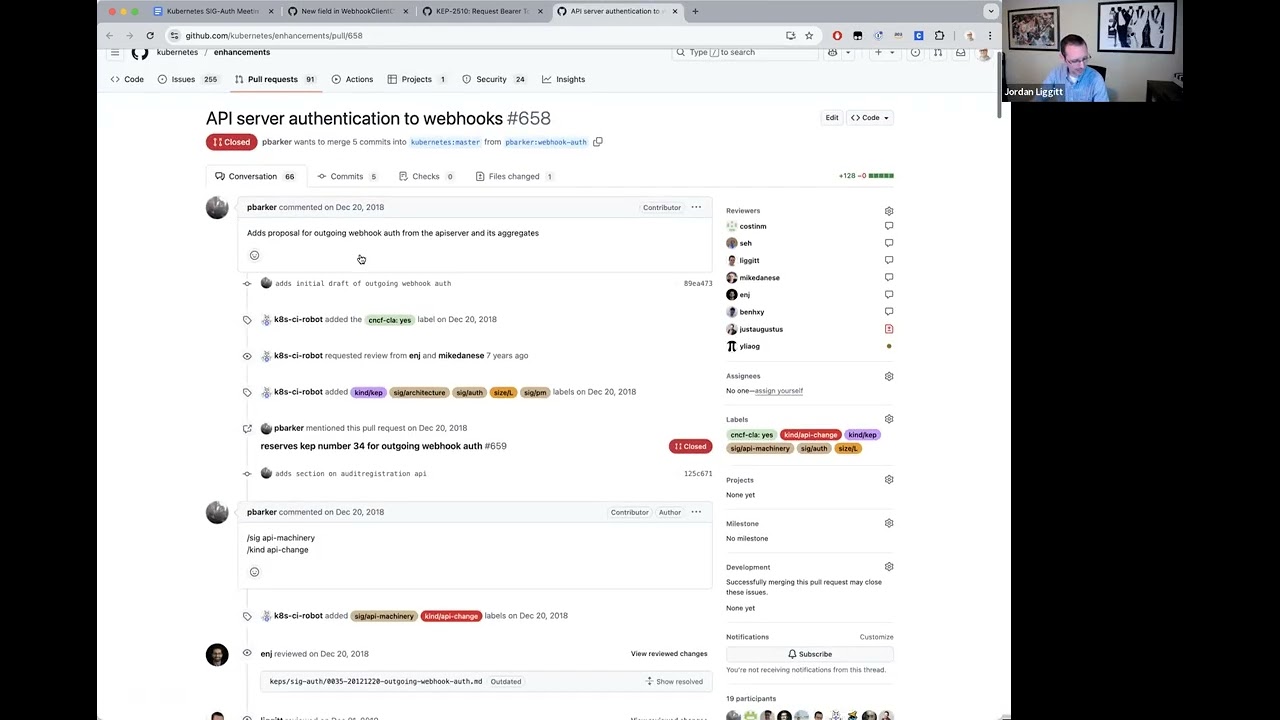
SIG-Auth bi-weekly meeting for 20250409
Source: YouTube · Kubernetes · published May 13, 2025 · 39:47
The video discusses the need for standardized, practical authentication in Kubernetes admission webhooks to mitigate security risks from unauthenticated access, especially in light of recent CVEs in the ingress engine. A key goal is to establish a minimal, widely applicable authentication model that works across cloud providers and cluster types, while avoiding overly complex or insecure solutions.
Key Takeaways:
• Current webhooks lack authentication by default, making them vulnerable to RCE and privacy leaks 1:00-1:23.
• Authentication mechanisms like TLS or service account tokens are viable, but must be designed to prevent hardcoded tokens from being exposed 2:55-3:09.
• A standardized, minimal approach—such as using audience-scoped service account tokens—is preferred over multiple options to reduce complexity for webhook developers 4:20-4:50.
• Cloud provider-specific authentication (e.g., GCP metadata server, AWS SDK) currently works but lacks portability and discoverability, highlighting a need for a unified standard 31:00-33:00.
• Cluster trust bundles and certificate generation are proposed as foundational infrastructure to support secure webhook communication 25:01-25:45.
The community recommends delaying implementation until core authentication features (like TLS validation and cluster trust bundles) are stable and widely available, emphasizing a practical, end-to-end solution that ensures security across all cluster environments.
Sources:
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Cybersecurity. Commonly maps to: Security and Risk Management, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
Welcome everyone to the April 9th meeting of SIG off. Uh we have a light agenda today. Um first up is Mo. Uh you put down it's time for us to talk about authentication of web hooks. Yeah. So I can get started. Um so I think probably everyone on this call is well familiar with the recent pile of ingress engine X CVES. Um the one I linked there is uh I think the relevant one for this discussion which is the rce on the admission controller. Uh and so certainly that admission controller should have been better designed such that an arbitrary request cannot cause an rce to it. Uh but uh the complete lack of authentication obviously makes it much worse because all you need is uh service level access sorry service network level access on the cluster. Uh which depending on how your networking is c…