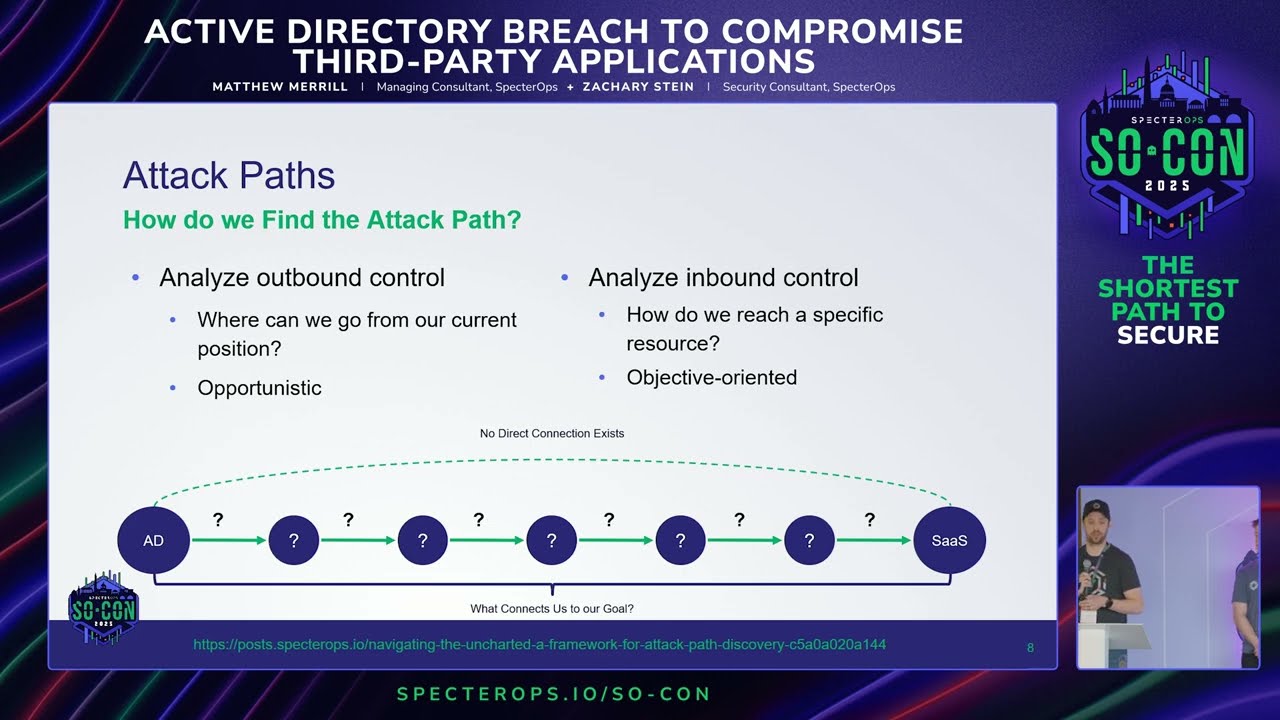
From AD to SaaS: Compromising Third-Party Applications from an Active Directory Breach | SO-CON 2025
Source: YouTube · SpecterOps · published May 7, 2025 · 33:11
Spectre Ops demonstrated how an attacker can bypass network segmentation and application-level security to compromise a third-party SAS application by exploiting ADCS and SCCM privileges to steal session cookies.
Key Takeaways:
• Attackers abused an ESC1 certificate template to impersonate an SCCM administrator, escalating from a standard domain user 11:00
• The team used SCCM to remotely execute a payload on a SAS administrator's workstation and dump Edge session cookies 18:30
• The attack exploited Clean Source Principle violations, allowing low-privilege users to enroll in high-privilege certificate templates 25:00
• Stolen cookies enabled direct authentication to the SAS application, completely bypassing separate passwords and MFA 28:00
• The case proves that AD compromise can lead to third-party application control even when those applications are technically isolated from Active Directory 32:00
Enforcing the Clean Source Principle and monitoring for ADCS abuse are essential to preventing attackers from bridging the gap between identity infrastructure and enterprise applications.
Sources:
- 11:00 Explanation of Clean Source Principle and attack path modeling.
- 18:30 Demonstration of using SCCM to execute payloads on target hosts.
- 25:00 Identification of CSP violations enabling the attack.
- 28:00 Demonstration of dumping session cookies and bypassing MFA.
- 32:00 Discussion on the risks of AD compromise to isolate
Generate CPE Credits
Generate a professional CPE document from this video's transcript.
Estimated credit: 0.5 CPE hours
Estimate uses the video runtime (1 hour ≈ 1 CPE, rounded to the nearest 0.5, minimum 0.5, maximum 2.0). The final amount can be lower after review, never higher.
Topic: Penetration Testing. Commonly maps to: Security Assessment and Testing, Security Operations. Exact CISSP domains are assigned during generation.
Free account. One generation at a time, with a daily limit.
CPEBuddy is independent and not affiliated with or endorsed by ISC2, ISACA, or any certification body. Exports are formatted for common CPE submissions; acceptance is at your certification body's discretion.
Transcript Preview
First 800 characters of the transcript
[Music] Thank you for joining our talk. Like she just said, this is from AD to SAS. So we're going to go over compromising an active directory environment and how we moved from that active directory environment to a third party SAS application. My name is Matthew Merrill. I am a adversary simulation operator, trainer, and manager here at Spectre Ops. Uh my background is primarily DoD. So I have a offensive and defensive perspective. I did some digital forensics and malware analysis and then I alo also have done red teams and pent test that as well. If you do the social media thing I melt 011 on pretty much most platforms I am on. And I'm Zachary Stein. I'm a senior consultant here at Spectre Ops. Uh similar to Matt minus the government work I also have done backgrounds in penetration and r…